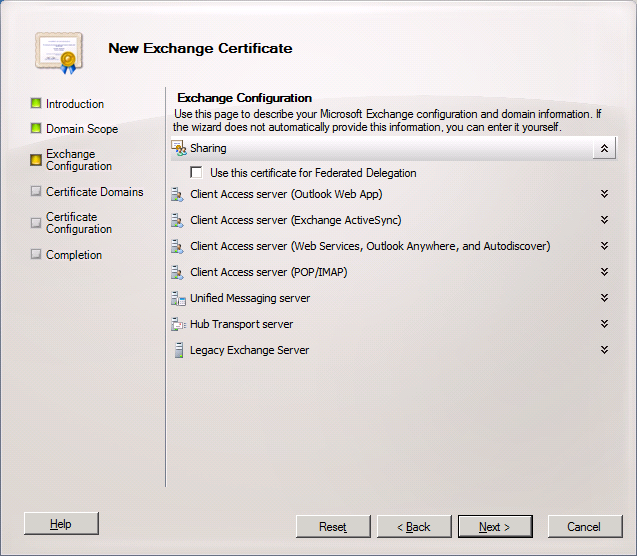
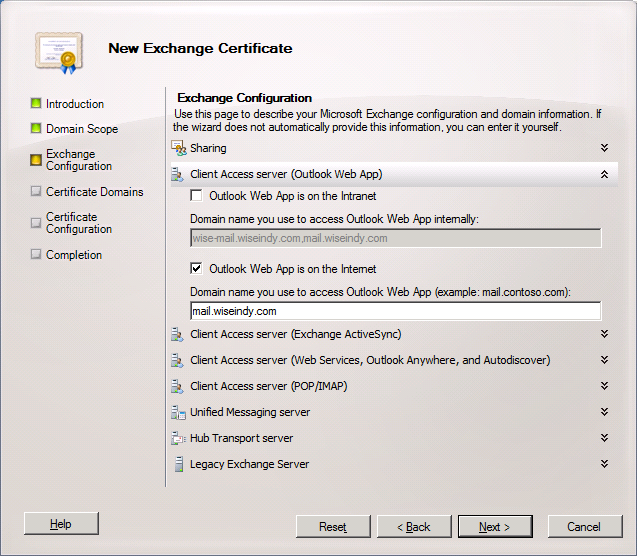
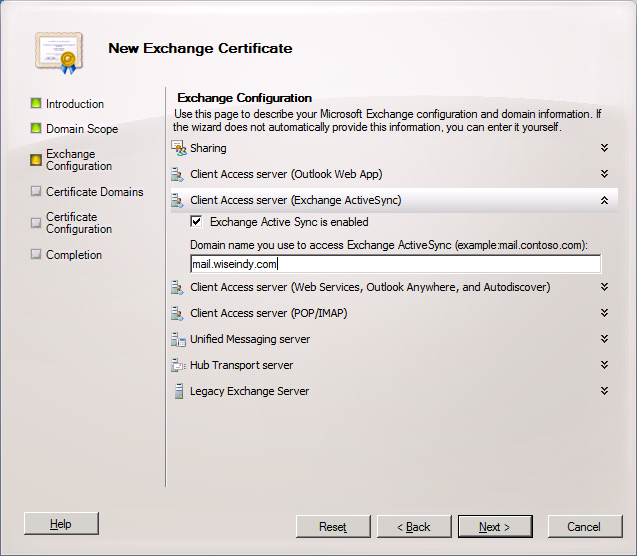
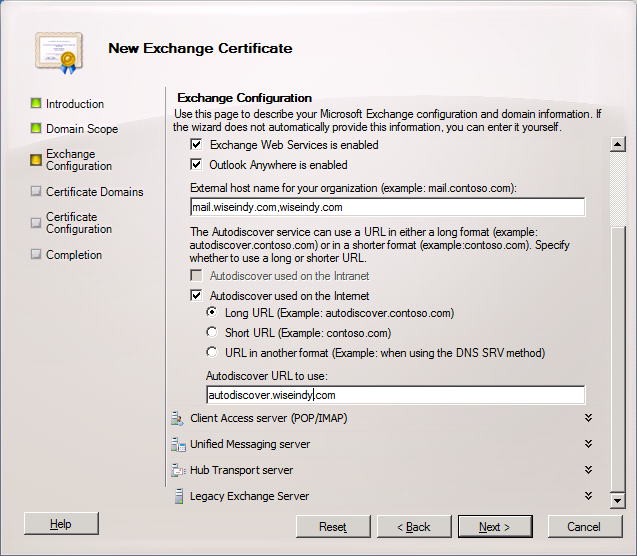
<?xml version="1.0" encoding="utf-8"?>
<feed xmlns="http://www.w3.org/2005/Atom">
<link href="https://wiseindy.com/feed.xml" rel="self" type="application/atom+xml"/>
<link href="https://wiseindy.com/" rel="alternate" type="text/html"/>
<updated>2019-02-21T15:03:00.000Z</updated>
<id>https://wiseindy.com/feed.xml</id>
<title type="html">Wiseindy</title>
<subtitle>Engineer by day, developer by night.</subtitle>
<author><name>Wiseindy</name></author>
<entry>
<title type="html">How to set DNS in CentOS/RHEL 7 &amp; prevent NetworkManager from overwriting /etc/resolv.conf?</title>
<link href="https://wiseindy.com/blog/linux/how-to-set-dns-in-centos-rhel-7-prevent-network-manager-from-overwriting-etc-resolv-conf/" rel="alternate" type="text/html" title="How to set DNS in CentOS/RHEL 7 &amp; prevent NetworkManager from overwriting /etc/resolv.conf?"/>
<published>2019-02-21T15:03:00.000Z</published>
<updated>2019-02-21T15:03:00.000Z</updated>
<id>https://wiseindy.com/blog/linux/how-to-set-dns-in-centos-rhel-7-prevent-network-manager-from-overwriting-etc-resolv-conf</id>
<content type="html" xml:base="https://wiseindy.com/blog/linux/how-to-set-dns-in-centos-rhel-7-prevent-network-manager-from-overwriting-etc-resolv-conf/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> CentOS 7 and RHEL 7 reached end of life in June 2024, so it’s time to move on to something newer if you haven’t already. The <code>dns=none</code> setting used below is still supported by NetworkManager, so this should still work on newer RHEL-based distros like Rocky Linux and AlmaLinux.</p>
</div>
<p>This guide shows you how to set custom DNS entries for CentOS 7 / RedHat 7 and ensure that the settings are persistent even after a reboot.</p>
<!--more-->
<h1 id="what-you-need">What you need</h1>
<ul>
<li>A CentOS 7 or a Red Hat Enterprise Linux (RHEL) 7 server</li>
<li>A couple of minutes</li>
</ul>
<h1 id="overview">Overview</h1>
<p>In CentOS and Red Hat Enterprise Linux (RHEL) 7, any custom DNS entries are stored in the file <code>/etc/resolv.conf</code>. However, if we simply go ahead and add our nameservers to this file, we’ll notice that after a reboot or a restart of the network.service, the file is overwritten by NetworkManager.</p>
<p>In this guide, we will first configure NetworkManager to <strong>not overwrite</strong> this file. Then, we will go ahead and actually add our custom nameservers to <code>/etc/resolv.conf</code>.</p>
<h1 id="step-1">Step 1</h1>
<p>The NetworkManager configuration is located here: <code>/etc/NetworkManager/NetworkManager.conf</code>
Open this file using <code>vim</code> or your favorite text editor.</p>
<p>Search for the <code>[main]</code> section in this file. It should look something like this:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="plaintext"><code><span class="line"><span>...</span></span>
<span class="line"><span>[main]</span></span>
<span class="line"><span>#plugins=ifcfg-rh,ibft</span></span>
<span class="line"><span>...</span></span></code></pre>
<p>Add <code>dns=none</code> just after the <code>[main]</code> tag like this:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="plaintext"><code><span class="line"><span>...</span></span>
<span class="line"><span>[main]</span></span>
<span class="line"><span>dns=none</span></span>
<span class="line"><span>#plugins=ifcfg-rh,ibft</span></span>
<span class="line"><span>...</span></span></code></pre>
<p>Go ahead and save the file.</p>
<h1 id="step-2">Step 2</h1>
<p>Let’s restart the <code>NetworkManager.service</code> service so that it picks up the changes we made to the configuration.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="plaintext"><code><span class="line"><span>sudo systemctl restart NetworkManager.service</span></span></code></pre>
<p>Note that the service name <code>NetworkManager.service</code> is <strong>case-sensitive</strong>.</p>
<h1 id="step-3">Step 3</h1>
<p>Now, let’s add our nameservers to <code>/etc/resolv.conf</code></p>
<p>Open this file in your favorite text editor and specify the name servers as follows:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="plaintext"><code><span class="line"><span># Generated by NetworkManager</span></span>
<span class="line"><span>nameserver 8.8.8.8</span></span>
<span class="line"><span>nameserver 8.8.4.4</span></span></code></pre>
<p>That’s it! You’re done. The nameservers added to <code>/etc/resolv.conf</code> will now persist even after a reboot. NetworkManager will no longer overwrite this file.</p>
<p class="credit">Header photo by <a href="https://unsplash.com/@steve_j">Steve Johnson</a> (via Unsplash)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Linux"/>
<category term="dns"/><category term="resolv.conf"/><category term="nameservers"/><category term="centos"/><category term="centos 7"/><category term="redhat"/><category term="rhel"/><category term="rhel 7"/><category term="redhat 7"/><category term="linux"/><category term="guides"/>
</entry>
<entry>
<title type="html">How to install OpenVPN server on Ubuntu 14.04 - A Step-by-Step Guide</title>
<link href="https://wiseindy.com/blog/linux/install-openvpn-ubuntu-1404/" rel="alternate" type="text/html" title="How to install OpenVPN server on Ubuntu 14.04 - A Step-by-Step Guide"/>
<published>2017-04-27T12:00:00.000Z</published>
<updated>2017-04-27T12:00:00.000Z</updated>
<id>https://wiseindy.com/blog/linux/install-openvpn-ubuntu-1404</id>
<content type="html" xml:base="https://wiseindy.com/blog/linux/install-openvpn-ubuntu-1404/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This guide is from 2017 and it’s starting to show its age. Ubuntu 14.04 reached end of life a long time ago, and newer versions of Easy-RSA don’t have the <code>build-ca</code> and <code>build-key</code> scripts used below anymore. The overall idea still holds, but if you’re setting up a VPN server today, start with a current Ubuntu LTS release and an up-to-date guide. Or take a look at WireGuard. It’s a lot simpler to set up.</p>
</div>
<p>This is a detailed &amp; step-by-step guide that will show you how to install and configure OpenVPN on Ubuntu 14.04. You can use OpenVPN to access the Internet safely and securely while on the move. To learn more about OpenVPN, you can check out the <a href="https://en.wikipedia.org/wiki/OpenVPN">Wikipedia link</a> or read about it on the <a href="https://openvpn.net/">official site</a></p>
<!--more-->
<h2 id="what-you-need">What you need:</h2>
<ul>
<li>An Ubuntu 14.04 system.</li>
<li>Root access</li>
<li>And as always, an internet connection</li>
</ul>
<p>This guide is split into 4 main sections.
Don’t worry if the titles look intimidating. If you follow the instructions, it should go smoothly and you should have a functioning OpenVPN server to which you can connect to from anywhere and using any device.</p>
<ol>
<li><a href="#part-1">Installation and configuration of OpenVPN server</a></li>
<li><a href="#part-2">Creating a Certificate Authority and Server-Side Certificate and Key</a></li>
<li><a href="#part-3">Generate Certificates and Keys for your devices</a></li>
<li><a href="#part-4">Create a Unified OpenVPN Profile for each of your devices</a></li>
</ol>
<h1 id="part-1">Part 1</h1>
<h2 id="installation-and-configuration-of-openvpn-server">Installation and configuration of OpenVPN server</h2>
<h3 id="step-11">Step 1.1:</h3>
<p>First, update your package lists and then install the <code>openvpn</code> and <code>easy-rsa</code> package.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> update</span></span>
<span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> openvpn</span><span style="color:#9ECBFF"> easy-rsa</span></span></code></pre>
<h3 id="step-12">Step 1.2:</h3>
<p>From now onwards, all the steps below have to be run as <code>root</code>. So, go ahead and login as root.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">su</span></span></code></pre>
<h3 id="step-13">Step 1.3:</h3>
<p>Let’s extract the sample VPN server configuration file to this location: <code>/etc/openvpn</code></p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">gunzip</span><span style="color:#79B8FF"> -c</span><span style="color:#9ECBFF"> /usr/share/doc/openvpn/examples/sample-config-files/server.conf.gz</span><span style="color:#F97583"> &gt;</span><span style="color:#9ECBFF"> /etc/openvpn/server.conf</span></span></code></pre>
<p><em>Note: <code>gunzip</code> is a utility that uncompresses a <code>gzip</code> file. <code>gz</code> or <code>.Z</code> is the extension for <code>gzip</code> files.</em></p>
<h3 id="step-14">Step 1.4:</h3>
<p>Still as root, open this file.</p>
<p>I prefer <code>vim</code> to open files on ubuntu. If you prefer <code>nano</code> instead, you can use that too.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">vi</span><span style="color:#9ECBFF"> /etc/openvpn/server.conf</span></span></code></pre>
<h3 id="step-15">Step 1.5:</h3>
<p>Now, we have to modify a few lines in this file.</p>
<p>Search for a section that looks like this</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Diffie hellman parameters.</span></span>
<span class="line"><span style="color:#6A737D"># Generate your own with:</span></span>
<span class="line"><span style="color:#6A737D">#   openssl dhparam -out dh1024.pem 1024</span></span>
<span class="line"><span style="color:#6A737D"># Substitute 2048 for 1024 if you are using</span></span>
<span class="line"><span style="color:#6A737D"># 2048 bit keys.</span></span>
<span class="line"><span style="color:#B392F0">dh</span><span style="color:#9ECBFF"> dh1024.pem</span></span></code></pre>
<p>Change <code>dh1024.pem</code> to <code>dh2048.pem</code>. This tells the server to use the stronger 2048-bit Diffie-Hellman parameters that we will generate later in the guide (Step 2.4).</p>
<h3 id="step-16">Step 1.6:</h3>
<p>Find and uncomment the line below. To uncomment, simply remove the semicolon <code>;</code> in front of the line.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># If enabled, this directive will configure</span></span>
<span class="line"><span style="color:#6A737D"># all clients to redirect their default</span></span>
<span class="line"><span style="color:#6A737D"># network gateway through the VPN, causing</span></span>
<span class="line"><span style="color:#6A737D"># all IP traffic such as web browsing and</span></span>
<span class="line"><span style="color:#6A737D"># and DNS lookups to go through the VPN</span></span>
<span class="line"><span style="color:#6A737D"># (The OpenVPN server machine may need to NAT</span></span>
<span class="line"><span style="color:#6A737D"># or bridge the TUN/TAP interface to the internet</span></span>
<span class="line"><span style="color:#6A737D"># in order for this to work properly).</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "redirect-gateway def1 bypass-dhcp"</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># If enabled, this directive will configure</span></span>
<span class="line"><span style="color:#6A737D"># all clients to redirect their default</span></span>
<span class="line"><span style="color:#6A737D"># network gateway through the VPN, causing</span></span>
<span class="line"><span style="color:#6A737D"># all IP traffic such as web browsing and</span></span>
<span class="line"><span style="color:#6A737D"># and DNS lookups to go through the VPN</span></span>
<span class="line"><span style="color:#6A737D"># (The OpenVPN server machine may need to NAT</span></span>
<span class="line"><span style="color:#6A737D"># or bridge the TUN/TAP interface to the internet</span></span>
<span class="line"><span style="color:#6A737D"># in order for this to work properly).</span></span>
<span class="line"><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "redirect-gateway def1 bypass-dhcp"</span></span></code></pre>
<p>This makes sure that the OpenVPN server will pass the client device’s web traffic to its destination.</p>
<h3 id="step-17">Step 1.7:</h3>
<p>Still in the same file, find and uncomment the following two lines. To uncomment, simply remove the semicolon <code>;</code> in front of the two lines.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Certain Windows-specific network settings</span></span>
<span class="line"><span style="color:#6A737D"># can be pushed to clients, such as DNS</span></span>
<span class="line"><span style="color:#6A737D"># or WINS server addresses.  CAVEAT:</span></span>
<span class="line"><span style="color:#6A737D"># http://openvpn.net/faq.html#dhcpcaveats</span></span>
<span class="line"><span style="color:#6A737D"># The addresses below refer to the public</span></span>
<span class="line"><span style="color:#6A737D"># DNS servers provided by opendns.com.</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "dhcp-option DNS 208.67.222.222"</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "dhcp-option DNS 208.67.220.220"</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Certain Windows-specific network settings</span></span>
<span class="line"><span style="color:#6A737D"># can be pushed to clients, such as DNS</span></span>
<span class="line"><span style="color:#6A737D"># or WINS server addresses.  CAVEAT:</span></span>
<span class="line"><span style="color:#6A737D"># http://openvpn.net/faq.html#dhcpcaveats</span></span>
<span class="line"><span style="color:#6A737D"># The addresses below refer to the public</span></span>
<span class="line"><span style="color:#6A737D"># DNS servers provided by opendns.com.</span></span>
<span class="line"><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "dhcp-option DNS 208.67.222.222"</span></span>
<span class="line"><span style="color:#B392F0">push</span><span style="color:#9ECBFF"> "dhcp-option DNS 208.67.220.220"</span></span></code></pre>
<p>The two IP addresses above belong to OpenDNS and will be used to lookup DNS request where possible. You can use any DNS service of your choice. Here we have used OpenDNS, and hence their IP addresses are listed in the file.</p>
<h3 id="step-18">Step 1.8:</h3>
<p>This is the last thing to change in the file. Look for this section below and uncomment the two lines by removing the semicolons <code>;</code></p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># You can uncomment this out on</span></span>
<span class="line"><span style="color:#6A737D"># non-Windows systems.</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">user</span><span style="color:#9ECBFF"> nobody</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">group</span><span style="color:#9ECBFF"> nogroup</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># You can uncomment this out on</span></span>
<span class="line"><span style="color:#6A737D"># non-Windows systems.</span></span>
<span class="line"><span style="color:#B392F0">user</span><span style="color:#9ECBFF"> nobody</span></span>
<span class="line"><span style="color:#B392F0">group</span><span style="color:#9ECBFF"> nogroup</span></span></code></pre>
<p>Save and close the file.</p>
<h3 id="step-19">Step 1.9:</h3>
<h4 id="packet-forwarding">Packet Forwarding</h4>
<p>We need to now enable an option that allows the server to forward traffic from client devices out to the Internet. If this is not done, the client traffic will stop at the server. To enable packet forwarding, run this command.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#79B8FF">echo</span><span style="color:#79B8FF"> 1</span><span style="color:#F97583"> &gt;</span><span style="color:#9ECBFF"> /proc/sys/net/ipv4/ip_forward</span></span></code></pre>
<p>This setting is not yet permanent and will not survive a reboot. To make it permanent, we need to edit the <code>sysctl.conf</code> file.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">vi</span><span style="color:#9ECBFF"> /etc/sysctl.conf</span></span></code></pre>
<p>In this file, find and uncomment the following line. To uncomment, remove the <code>#</code> in front of the line.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Uncomment the next line to enable packet forwarding for IPv4</span></span>
<span class="line"><span style="color:#6A737D">#net.ipv4.ip_forward=1</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Uncomment the next line to enable packet forwarding for IPv4</span></span>
<span class="line"><span style="color:#B392F0">net.ipv4.ip_forward</span><span style="color:#9ECBFF">=1</span></span></code></pre>
<p>Save the file and exit.</p>
<h3 id="step-110">Step 1.10:</h3>
<h4 id="set-up-firewall-rules-in-the-uncomplicated-firewall-ufw">Set up firewall rules in the Uncomplicated Firewall (ufw)</h4>
<p>We will be using OpenVPN over UDP, so the firewall must allow UDP traffic over port <strong>1194</strong>.</p>
<p>Still as root, enter the following command:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">ufw</span><span style="color:#9ECBFF"> allow</span><span style="color:#9ECBFF"> 1194/udp</span></span></code></pre>
<p>Open the firewall’s (ufw) primary configuration file. We have to set the firewall forwarding policy.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">vi</span><span style="color:#9ECBFF"> /etc/default/ufw</span></span></code></pre>
<p>Search for the string <code>DEFAULT_FORWARD_POLICY="DROP"</code> in this file. Change the <code>DROP</code> to <code>ACCEPT</code>.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#E1E4E8">DEFAULT_FORWARD_POLICY</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"DROP"</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#E1E4E8">DEFAULT_FORWARD_POLICY</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"ACCEPT"</span></span></code></pre>
<p>Save the file and exit.</p>
<h3 id="step-111">Step 1.11:</h3>
<p>There’s one more step before we can move on to the next section.</p>
<p>We need to add additional firewall rules.</p>
<p>Open this file</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">vi</span><span style="color:#9ECBFF"> /etc/ufw/before.rules</span></span></code></pre>
<p>We will be adding rules for NAT (network address translation) and IP masquerading of connected devices.</p>
<p>Modify this file to look like this.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"><span style="color:#6A737D"># rules.before</span></span>
<span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"><span style="color:#6A737D"># Rules that should be run before the ufw command line added rules. Custom</span></span>
<span class="line"><span style="color:#6A737D"># rules should be added to one of these chains:</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-input</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-output</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-forward</span></span>
<span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"></span>
<span class="line"><span style="color:#6A737D"># Don't delete these required lines, otherwise there will be errors</span></span>
<span class="line"><span style="color:#F97583">*</span><span style="color:#E1E4E8">filter</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"><span style="color:#6A737D"># rules.before</span></span>
<span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"><span style="color:#6A737D"># Rules that should be run before the ufw command line added rules. Custom</span></span>
<span class="line"><span style="color:#6A737D"># rules should be added to one of these chains:</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-input</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-output</span></span>
<span class="line"><span style="color:#6A737D">#   ufw-before-forward</span></span>
<span class="line"><span style="color:#6A737D">#</span></span>
<span class="line"></span>
<span class="line"><span style="color:#6A737D">#################################</span></span>
<span class="line"><span style="color:#6A737D"># START OPENVPN RULES</span></span>
<span class="line"><span style="color:#6A737D"># NAT table rules</span></span>
<span class="line"><span style="color:#F97583">*</span><span style="color:#E1E4E8">nat</span></span>
<span class="line"><span style="color:#B392F0">:POSTROUTING</span><span style="color:#9ECBFF"> ACCEPT</span><span style="color:#E1E4E8"> [0:0] </span></span>
<span class="line"><span style="color:#6A737D"># Allow traffic from OpenVPN client to eth0</span></span>
<span class="line"><span style="color:#B392F0">-A</span><span style="color:#9ECBFF"> POSTROUTING</span><span style="color:#79B8FF"> -s</span><span style="color:#9ECBFF"> 10.8.0.0/24</span><span style="color:#79B8FF"> -o</span><span style="color:#9ECBFF"> eth0</span><span style="color:#79B8FF"> -j</span><span style="color:#9ECBFF"> MASQUERADE</span></span>
<span class="line"><span style="color:#B392F0">COMMIT</span></span>
<span class="line"><span style="color:#6A737D"># END OPENVPN RULES</span></span>
<span class="line"><span style="color:#6A737D">#################################</span></span>
<span class="line"></span>
<span class="line"><span style="color:#6A737D"># Don't delete these required lines, otherwise there will be errors</span></span>
<span class="line"><span style="color:#F97583">*</span><span style="color:#E1E4E8">filter</span></span></code></pre>
<p>Once you’ve added the section, enable the firewall (ufw).</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">ufw</span><span style="color:#9ECBFF"> enable</span></span></code></pre>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h1 id="part-2">Part 2</h1>
<h2 id="creating-a-certificate-authority-and-server-side-certificate-and-key">Creating a Certificate Authority and Server-Side Certificate and Key</h2>
<p>Okay, so we have installed and configured OpenVPN and the firewall settings in the above section. Now, let’s go ahead and create certificates and keys for our new OpenVPN server.</p>
<h4 id="creating-a-certificate-authority-ca">Creating a certificate authority (CA)</h4>
<h3 id="step-21">Step 2.1:</h3>
<p>Make sure you’re still logged in as root.</p>
<p>Copy the Easy-RSA generation scripts to <code>/etc/openvpn</code></p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">cp</span><span style="color:#79B8FF"> -r</span><span style="color:#9ECBFF"> /usr/share/easy-rsa/</span><span style="color:#9ECBFF"> /etc/openvpn</span></span></code></pre>
<h3 id="step-22">Step 2.2:</h3>
<p>Now, create a directory to store our keys.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">mkdir</span><span style="color:#9ECBFF"> /etc/openvpn/easy-rsa/keys</span></span></code></pre>
<h3 id="step-23">Step 2.3:</h3>
<p>Now we will edit the <code>vars</code> file (<code>/etc/openvpn/easy-rsa/vars</code>) and add in some default values for a person or a business. The information that is entered into this file will be copied to the certificates and keys and will help us in identifying them later.</p>
<p>You can put in any values you like. Here is an example.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_COUNTRY</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"CA"</span></span>
<span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_PROVINCE</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"ON"</span></span>
<span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_CITY</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"Toronto"</span></span>
<span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_ORG</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"Wiseindy"</span></span>
<span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_EMAIL</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"wiseindy@example.com"</span></span>
<span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_OU</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"WiseOU"</span></span></code></pre>
<p>There is one more line to edit in this file before you close it. We need to set the default filename for the server key and certificate. In this tutorial we’ve used the name <code>server</code> for simplicity. If you’re using a different name, please make sure you replace <code>server</code> with your custom name in the commands.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#F97583">export</span><span style="color:#E1E4E8"> KEY_NAME</span><span style="color:#F97583">=</span><span style="color:#9ECBFF">"server"</span></span></code></pre>
<p>Save and close the file.</p>
<h3 id="step-24">Step 2.4:</h3>
<p>The next step is to generate the Diffie-Hellman parameters.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">openssl</span><span style="color:#9ECBFF"> dhparam</span><span style="color:#79B8FF"> -out</span><span style="color:#9ECBFF"> /etc/openvpn/dh2048.pem</span><span style="color:#79B8FF"> 2048</span></span></code></pre>
<h3 id="step-25">Step 2.5:</h3>
<p>Now, navigate to the <code>easy-rsa</code> directory.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#79B8FF">cd</span><span style="color:#9ECBFF"> /etc/openvpn/easy-rsa</span></span></code></pre>
<h3 id="step-26">Step 2.6:</h3>
<p>Once you’re in the <code>easy-rsa</code> directory, run the following command to initialize the PKI (Public Key Infrastructure).</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#79B8FF">.</span><span style="color:#9ECBFF"> ./vars</span></span></code></pre>
<p>Note the <code>.</code> (dot) and <code> </code> (space) in front of <code>./vars</code>.</p>
<p>The above command will output the following:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">NOTE:</span><span style="color:#9ECBFF"> If</span><span style="color:#9ECBFF"> you</span><span style="color:#9ECBFF"> run</span><span style="color:#9ECBFF"> ./clean-all,</span><span style="color:#9ECBFF"> I</span><span style="color:#9ECBFF"> will</span><span style="color:#9ECBFF"> be</span><span style="color:#9ECBFF"> doing</span><span style="color:#9ECBFF"> a</span><span style="color:#9ECBFF"> rm</span><span style="color:#79B8FF"> -rf</span><span style="color:#9ECBFF"> on</span><span style="color:#9ECBFF"> /etc/openvpn/easy-rsa/keys</span></span></code></pre>
<p>You can ignore this warning message since we haven’t yet generated anything.</p>
<h3 id="step-27">Step 2.7:</h3>
<p>Let’s clear the working directory of any example keys and start fresh.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">./clean-all</span></span></code></pre>
<h3 id="step-28">Step 2.8:</h3>
<p>We are all set to create our certificate authority now. When you run the following command, it will ask you to confirm the values you had entered in the <code>vars</code> file in step 2.3. Hit enter to confirm the values.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">./build-ca</span></span></code></pre>
<h4 id="generate-a-certificate-and-key-for-the-server">Generate a Certificate and Key for the Server</h4>
<h3 id="step-29">Step 2.9:</h3>
<p>Well, we now have a certificate authority (CA) set up. Let’s build our server key now.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">./build-key-server</span><span style="color:#9ECBFF"> server</span></span></code></pre>
<p><em>Note: Note that I’ve used the name <strong>server</strong> in the above command. This is because I’ve set <code>export KEY_NAME="server"</code> in the <code>vars</code> file (step 2.3). If you’ve used a different name, make sure you modify the command accordingly</em></p>
<p>When you run this command, you’ll see a similar output as the previous step. You can hit enter to confirm them. However, this time you will see two additional prompts.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">Please</span><span style="color:#9ECBFF"> enter</span><span style="color:#9ECBFF"> the</span><span style="color:#9ECBFF"> following</span><span style="color:#9ECBFF"> 'extra'</span><span style="color:#9ECBFF"> attributes</span></span>
<span class="line"><span style="color:#B392F0">to</span><span style="color:#9ECBFF"> be</span><span style="color:#9ECBFF"> sent</span><span style="color:#9ECBFF"> with</span><span style="color:#9ECBFF"> your</span><span style="color:#9ECBFF"> certificate</span><span style="color:#9ECBFF"> request</span></span>
<span class="line"><span style="color:#B392F0">A</span><span style="color:#9ECBFF"> challenge</span><span style="color:#9ECBFF"> password</span><span style="color:#E1E4E8"> []:</span></span>
<span class="line"><span style="color:#B392F0">An</span><span style="color:#9ECBFF"> optional</span><span style="color:#9ECBFF"> company</span><span style="color:#9ECBFF"> name</span><span style="color:#E1E4E8"> []:</span></span></code></pre>
<p>Both of these should be left blank. Hit Enter to continue.</p>
<p>When it prompts you to sign the certificate and commit, type <code>y</code> for both the prompts and hit enter.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">Sign</span><span style="color:#9ECBFF"> the</span><span style="color:#9ECBFF"> certificate?</span><span style="color:#E1E4E8"> [y/n]  y</span></span>
<span class="line"><span style="color:#B392F0">1</span><span style="color:#9ECBFF"> out</span><span style="color:#9ECBFF"> of</span><span style="color:#79B8FF"> 1</span><span style="color:#9ECBFF"> certificate</span><span style="color:#9ECBFF"> requests</span><span style="color:#9ECBFF"> certified,</span><span style="color:#9ECBFF"> commit?</span><span style="color:#E1E4E8"> [y/n]  y</span></span></code></pre>
<p>Now you should see the following output. This means that all is good so far.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">Write</span><span style="color:#9ECBFF"> out</span><span style="color:#9ECBFF"> database</span><span style="color:#9ECBFF"> with</span><span style="color:#79B8FF"> 1</span><span style="color:#9ECBFF"> new</span><span style="color:#9ECBFF"> entries</span></span>
<span class="line"><span style="color:#B392F0">Data</span><span style="color:#9ECBFF"> Base</span><span style="color:#9ECBFF"> Updated</span></span></code></pre>
<h3 id="step-210">Step 2.10</h3>
<h4 id="move-the-server-certificates-and-keys">Move the Server Certificates and Keys</h4>
<p>Well, we’ve now generated the server CA, keys and certificate. Let’s copy these over to the correct location <code>/etc/openvpn/</code>.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">cp</span><span style="color:#9ECBFF"> /etc/openvpn/easy-rsa/keys/{server.crt,server.key,ca.crt}</span><span style="color:#9ECBFF"> /etc/openvpn</span></span></code></pre>
<h3 id="step-211">Step 2.11</h3>
<p>Well, guess what? Our OpenVPN server is ready now. Let’s start it.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">service</span><span style="color:#9ECBFF"> openvpn</span><span style="color:#9ECBFF"> start</span></span></code></pre>
<h1 id="part-3">Part 3</h1>
<h2 id="generate-certificates-and-keys-for-your-devices">Generate Certificates and Keys for your devices</h2>
<p>In the previous section, we created the key and certificate for our server. We are going to do that for our devices now.</p>
<p>We will build one for a client device called <code>myphone</code>. You can name your client device anything. Just make sure to substitute the name in the commands that follow.</p>
<h3 id="step-31">Step 3.1:</h3>
<p>You should still be root and still working from this directory <code>/etc/openvpn/easy-rsa</code>.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">./build-key</span><span style="color:#9ECBFF"> myphone</span></span></code></pre>
<p>Like in the previous steps, you’ll be asked to confirm the Distinguished Name variables. Hit enter to accept the defaults.</p>
<h3 id="step-32">Step 3.2:</h3>
<p>Now copy the sample client configuration file to the <code>easy-rsa/keys</code> directory. This file will be used as a template. We will be editing this template file for each of our devices.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">cp</span><span style="color:#9ECBFF"> /usr/share/doc/openvpn/examples/sample-config-files/client.conf</span><span style="color:#9ECBFF"> /etc/openvpn/easy-rsa/keys/myphone.ovpn</span></span></code></pre>
<p>You can repeat this section (steps 3.1 and 3.2) for each client device. Just make sure you use a different name for each of your devices (in this case we’ve used <code>myphone</code>)</p>
<h1 id="part-4">Part 4</h1>
<h2 id="create-a-unified-openvpn-profile-for-each-of-your-devices">Create a Unified OpenVPN Profile for each of your devices</h2>
<p>Now that you have created keys and certificates for your device <code>myphone</code>, let’s create one unified <code>.ovpn</code> file which will contain all this information.</p>
<h3 id="step-41">Step 4.1:</h3>
<p>From the <code>/etc/openvpn/easy-rsa</code> directory, copy the following files to your computer (the one you’re reading this article on). We will be editing these in a text editor (Notepad, TextEdit, etc.).</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">myphone.crt</span></span>
<span class="line"><span style="color:#B392F0">myphone.key</span></span>
<span class="line"><span style="color:#B392F0">myphone.ovpn</span></span>
<span class="line"><span style="color:#B392F0">ca.crt</span></span></code></pre>
<h3 id="step-42">Step 4.2</h3>
<p>Open the <code>myphone.ovpn</code> file in a text editor like Notepad (Windows) or TextEdit (macOS) or whatever you prefer, really.</p>
<p>Add your server’s IP address to the this section in the beginning of the file. Replace <code>my-server-1</code> with your server’s IP address.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># The hostname/IP and port of the server.</span></span>
<span class="line"><span style="color:#6A737D"># You can have multiple remote entries</span></span>
<span class="line"><span style="color:#6A737D"># to load balance between the servers.</span></span>
<span class="line"><span style="color:#B392F0">remote</span><span style="color:#9ECBFF"> my-server-1</span><span style="color:#79B8FF"> 1194</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># The hostname/IP and port of the server.</span></span>
<span class="line"><span style="color:#6A737D"># You can have multiple remote entries</span></span>
<span class="line"><span style="color:#6A737D"># to load balance between the servers.</span></span>
<span class="line"><span style="color:#B392F0">remote</span><span style="color:#79B8FF"> 203.0.113.10</span><span style="color:#79B8FF"> 1194</span></span></code></pre>
<h3 id="step-43">Step 4.3</h3>
<p>In the same file, scroll down and uncomment this section (This doesn’t apply to Windows, so you can skip it if you’re going to use this VPN profile on a Windows machine).</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Downgrade privileges after initialization (non-Windows only)</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">user</span><span style="color:#9ECBFF"> nobody</span></span>
<span class="line"><span style="color:#E1E4E8">;</span><span style="color:#B392F0">group</span><span style="color:#9ECBFF"> nogroup</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Downgrade privileges after initialization (non-Windows only)</span></span>
<span class="line"><span style="color:#B392F0">user</span><span style="color:#9ECBFF"> nobody</span></span>
<span class="line"><span style="color:#B392F0">group</span><span style="color:#9ECBFF"> nogroup</span></span></code></pre>
<h3 id="step-44">Step 4.4:</h3>
<p>Scroll further down and this time you’ll <strong>comment</strong> a few lines instead of uncommenting. We do this because we are directly including the <code>.crt</code> and <code>.key</code> files within this <code>.ovpn</code> file.</p>
<p>Before:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># SSL/TLS parms.</span></span>
<span class="line"><span style="color:#6A737D"># . . .</span></span>
<span class="line"><span style="color:#B392F0">ca</span><span style="color:#9ECBFF"> ca.crt</span></span>
<span class="line"><span style="color:#B392F0">cert</span><span style="color:#9ECBFF"> client.crt</span></span>
<span class="line"><span style="color:#B392F0">key</span><span style="color:#9ECBFF"> client.key</span></span></code></pre>
<p>After:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># SSL/TLS parms.</span></span>
<span class="line"><span style="color:#6A737D"># . . .</span></span>
<span class="line"><span style="color:#6A737D">#ca ca.crt</span></span>
<span class="line"><span style="color:#6A737D">#cert client.crt</span></span>
<span class="line"><span style="color:#6A737D">#key client.key</span></span></code></pre>
<h3 id="step-45">Step 4.5:</h3>
<p>At the end of the file, add this text to block outside DNS</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Prevent DNS leak</span></span>
<span class="line"><span style="color:#B392F0">block-outside-dns</span></span></code></pre>
<h3 id="step-46">Step 4.6:</h3>
<p>Now, at the end of the file, we will be copying and pasting the contents of <code>ca.crt</code>, <code>myphone.crt</code>, and <code>myphone.key</code> files.</p>
<p>Open the <code>.crt</code> and <code>.key</code> files in a text editor and copy-paste the content as shown below</p>
<p>This is how we will be doing it.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">ca</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#E1E4E8">  (</span><span style="color:#B392F0">insert</span><span style="color:#9ECBFF"> ca.crt</span><span style="color:#9ECBFF"> here</span><span style="color:#E1E4E8">)</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/ca</span><span style="color:#F97583">&gt;</span></span>
<span class="line"></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">cert</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#E1E4E8">  (</span><span style="color:#B392F0">insert</span><span style="color:#9ECBFF"> myphone.crt</span><span style="color:#9ECBFF"> here</span><span style="color:#E1E4E8">)</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/cert</span><span style="color:#F97583">&gt;</span></span>
<span class="line"></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">key</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#E1E4E8">  (</span><span style="color:#B392F0">insert</span><span style="color:#9ECBFF"> myphone.key</span><span style="color:#9ECBFF"> here</span><span style="color:#E1E4E8">)</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/key</span><span style="color:#F97583">&gt;</span></span></code></pre>
<p>Once you’re done copy-pasting the content, the end of your <code>.ovpn</code> file should look like this:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">ca</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#B392F0">-----BEGIN</span><span style="color:#9ECBFF"> CERTIFICATE-----</span></span>
<span class="line"><span style="color:#79B8FF">.</span><span style="color:#9ECBFF"> .</span><span style="color:#9ECBFF"> .</span></span>
<span class="line"><span style="color:#B392F0">-----END</span><span style="color:#9ECBFF"> CERTIFICATE-----</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/ca</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#E1E4E8">  </span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">cert</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#B392F0">Certificate:</span></span>
<span class="line"><span style="color:#79B8FF">.</span><span style="color:#9ECBFF"> .</span><span style="color:#9ECBFF"> .</span></span>
<span class="line"><span style="color:#B392F0">-----END</span><span style="color:#9ECBFF"> CERTIFICATE-----</span></span>
<span class="line"><span style="color:#79B8FF">.</span><span style="color:#9ECBFF"> .</span><span style="color:#9ECBFF"> .</span></span>
<span class="line"><span style="color:#B392F0">-----END</span><span style="color:#9ECBFF"> CERTIFICATE-----</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/cert</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#E1E4E8">  </span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">key</span><span style="color:#F97583">&gt;</span></span>
<span class="line"><span style="color:#B392F0">-----BEGIN</span><span style="color:#9ECBFF"> PRIVATE</span><span style="color:#9ECBFF"> KEY-----</span></span>
<span class="line"><span style="color:#79B8FF">.</span><span style="color:#9ECBFF"> .</span><span style="color:#9ECBFF"> .</span></span>
<span class="line"><span style="color:#B392F0">-----END</span><span style="color:#9ECBFF"> PRIVATE</span><span style="color:#9ECBFF"> KEY-----</span></span>
<span class="line"><span style="color:#F97583">&lt;</span><span style="color:#E1E4E8">/key</span><span style="color:#F97583">&gt;</span></span></code></pre>
<p>Save the changes and close the file.</p>
<h3 id="step-47">Step 4.7:</h3>
<h4 id="windows">Windows</h4>
<p>If you’re using Windows, install the official <a href="https://openvpn.net/index.php/open-source/downloads.html">OpenVPN client from here</a>.
After installation, paste your <code>myphone.ovpn</code> file here <code>C:\Program Files\OpenVPN\config\</code>.</p>
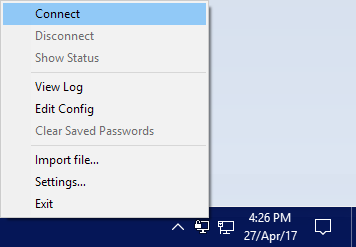
<p>To connect to your VPN server, right-click the OpenVPN client in the taskbar and click <strong>Connect</strong>.</p>
<p><img src="/assets/images/posts/2017-04-27-install-openvpn-ubuntu-1404-001.png" alt="Connect to OpenVPN" title="Connect to OpenVPN"></p>
<p>To verify if you’re connected, go to <a href="https://google.com">Google</a> and type <code>What is my IP</code>. If it returns the IP address of your OpenVPN server, all is well and your VPN is working as expected.</p>
<h4 id="macos">macOS</h4>
<p>For macOS, install <a href="https://tunnelblick.net/downloads.html">Tunnelblick</a> and import your <code>.ovpn</code> profile.
<strong>Note:</strong> If you get an error and Tunnelblick is unable to connect, remove the following text from your <code>.ovpn</code> profile.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Prevent DNS leak</span></span>
<span class="line"><span style="color:#B392F0">block-outside-dns</span></span></code></pre>
<h4 id="android">Android</h4>
<p>For Android, download the <a href="https://play.google.com/store/apps/details?id=net.openvpn.openvpn&amp;hl=en">OpenVPN Connect app from the Google Play Store</a>. Import your <code>.ovpn</code> profile and you’re all set!</p>
<h4 id="ios">iOS</h4>
<p>For iPhone and iPad, download the <a href="https://itunes.apple.com/us/app/openvpn-connect/id590379981?mt=8">OpenVPN Connect app from the Apple App Store</a>. Import your <code>.ovpn</code> profile and you’re all set!</p>
<p>Guess what? You’re done.</p>
<p>I recommend you create separate <code>.ovpn</code> files for each of your devices instead of using the same key &amp; certificate for everything.</p>
<p><strong>To create <code>.ovpn</code> profiles for more devices, <a href="#part-3">repeat steps from part 3 onwards</a>.</strong></p>
<p class="credit">Header photo: <a href="https://commons.wikimedia.org/wiki/File:Old_key_in_door_lock.jpg">Old key in door lock</a> by Santeri Viinamäki (<a href="https://creativecommons.org/licenses/by-sa/4.0/">CC BY-SA 4.0</a>, via Wikimedia Commons)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Linux"/>
<category term="openvpn"/><category term="ubuntu 14.04"/><category term="ubuntu"/><category term="guide"/><category term="linux"/><category term="vpn"/><category term="pia"/><category term="vps"/><category term="guides"/>
</entry>
<entry>
<title type="html">How to install Jekyll on Ubuntu 16.04 or Windows 10 - A Step-by-Step Guide</title>
<link href="https://wiseindy.com/blog/linux/install-jekyll-on-ubuntu-16.04-windows-10/" rel="alternate" type="text/html" title="How to install Jekyll on Ubuntu 16.04 or Windows 10 - A Step-by-Step Guide"/>
<published>2017-04-26T11:00:00.000Z</published>
<updated>2017-04-26T11:00:00.000Z</updated>
<id>https://wiseindy.com/blog/linux/install-jekyll-on-ubuntu-16.04-windows-10</id>
<content type="html" xml:base="https://wiseindy.com/blog/linux/install-jekyll-on-ubuntu-16.04-windows-10/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This guide is from 2017 and it’s pretty outdated now. Ubuntu 16.04 and Ruby 2.3 are both long past end of life, and current versions of Jekyll need a much newer Ruby. These days you can skip the PPA entirely: install <code>ruby-full</code> and <code>build-essential</code> from your distro’s packages and follow the <a href="https://jekyllrb.com/docs/installation/ubuntu/">official Jekyll guide for Ubuntu</a>.</p>
</div>
<p>This guide will show you step by step how to install Jekyll 3.4.3 on a machine running Ubuntu or Windows 10.
<a href="https://jekyllrb.com/docs/installation/">Jekyll’s official guide</a> is good, but it’s very basic and doesn’t explain how to install Ruby, RubyGems and other dependencies.</p>
<!--more-->
<h2 id="what-you-need">What you need:</h2>
<ul>
<li>An Ubuntu 16.04 or Windows 10 system. This guide should also work for older Ubuntu 14.04</li>
<li>And as always, an internet connection</li>
</ul>
<h2 id="step-1">Step 1:</h2>
<p>Skip to step 2 if you’re installing Jekyll on Ubuntu.</p>
<p>To install Jekyll on Windows 10, we need to first enable <strong>Windows Subsystem on Linux</strong>. <a href="/blog/windows/enabling-linux-bash-shell-in-windows-10/">Here is a detailed guide that will show you how to do this step-by-step.</a></p>
<h2 id="step-2">Step 2:</h2>
<p>We will now install <strong>ruby2.3</strong>. To do so, we have to first add the brightbox repository. When asked whether you want to confirm adding the repository, hit ENTER to proceed.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-add-repository</span><span style="color:#9ECBFF"> ppa:brightbox/ruby-ng</span></span>
<span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> update</span></span></code></pre>
<p>Install <strong>ruby2.3</strong></p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> ruby2.3</span><span style="color:#9ECBFF"> ruby2.3-dev</span></span></code></pre>
<p>Now you should have <strong>Ruby</strong> and <strong>RubyGems</strong> installed which are the prerequisite for installing Jekyll.</p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h2 id="step-3">Step 3:</h2>
<p>Install <a href="https://gcc.gnu.org/install/">GCC</a> and <a href="https://www.gnu.org/software/make/">Make</a></p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> gcc</span><span style="color:#9ECBFF"> make</span><span style="color:#79B8FF"> -y</span></span></code></pre>
<h2 id="step-4">Step 4:</h2>
<p>Install Jekyll and Bundler gems</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> gem</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> jekyll</span></span></code></pre>
<p>Guess what? That’s it. You have Jekyll 3.4.3 installed.</p>
<h2 id="further-information">Further information:</h2>
<p>Here are some commands from <a href="https://jekyllrb.com/docs/quickstart/">jekyllrb.com</a> that should get you up and running with a new blog.</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Create a new Jekyll site at ./wiseblog</span></span>
<span class="line"><span style="color:#B392F0">jekyll</span><span style="color:#9ECBFF"> new</span><span style="color:#9ECBFF"> wiseblog</span></span></code></pre>
<p>To build this site:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#6A737D"># Change into your new directory</span></span>
<span class="line"><span style="color:#79B8FF">cd</span><span style="color:#9ECBFF"> wiseblog</span></span>
<span class="line"></span>
<span class="line"><span style="color:#6A737D"># Build the site and preview it</span></span>
<span class="line"><span style="color:#B392F0">bundle</span><span style="color:#9ECBFF"> exec</span><span style="color:#9ECBFF"> jekyll</span><span style="color:#9ECBFF"> serve</span></span></code></pre>
<p><strong>Note:</strong> If you’re running Windows, you may get an error when you try to run <code>bundle exec jekyll serve</code>. In this case, simply run it with the <code>--force_polling</code> option as follows:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">bundle</span><span style="color:#9ECBFF"> exec</span><span style="color:#9ECBFF"> jekyll</span><span style="color:#9ECBFF"> serve</span><span style="color:#79B8FF"> --force_polling</span></span></code></pre>
<p>Now you can preview your website on <code>http://localhost:4000</code></p>
<h2 id="notes">Notes:</h2>
<p>(You can skip this part. This is only for my reference and for anyone who faces a similar issue)</p>
<p>I had to install <a href="https://github.com/sparklemotion/nokogiri">Nokogiri</a> for my site and was having issues. This is how I solved it.</p>
<p>Below are the installation instructions on <a href="https://www.nokogiri.org/tutorials/installing_nokogiri.html">nokogiri.org</a>:</p>
<pre class="astro-code github-dark" style="background-color:#24292e;color:#e1e4e8; overflow-x: auto;" tabindex="0" data-language="shell"><code><span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> build-essential</span><span style="color:#9ECBFF"> patch</span></span>
<span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> apt-get</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> ruby-dev</span><span style="color:#9ECBFF"> zlib1g-dev</span><span style="color:#9ECBFF"> liblzma-dev</span></span>
<span class="line"><span style="color:#B392F0">sudo</span><span style="color:#9ECBFF"> gem</span><span style="color:#9ECBFF"> install</span><span style="color:#9ECBFF"> nokogiri</span></span></code></pre>
<p class="credit">Header photo by <a href="https://stocksnap.io/photo/wood-typewriter-VV0697QWMS">Dustin Lee</a> (CC0, via StockSnap)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Linux"/>
<category term="jekyll"/><category term="jekyllrb"/><category term="ruby"/><category term="ruby2.3"/><category term="ubuntu 16.04"/><category term="ubuntu 14.04"/><category term="ubuntu"/><category term="guide"/><category term="linux"/><category term="ubuntu"/><category term="static"/><category term="static site generator"/><category term="Guides"/>
</entry>
<entry>
<title type="html">How to fix error 0x80004005 - Cannot enable developer mode in Windows 10</title>
<link href="https://wiseindy.com/blog/windows/windows-10-developer-mode-fix-error-0x80004005/" rel="alternate" type="text/html" title="How to fix error 0x80004005 - Cannot enable developer mode in Windows 10"/>
<published>2017-04-26T10:00:00.000Z</published>
<updated>2017-04-26T10:00:00.000Z</updated>
<id>https://wiseindy.com/blog/windows/windows-10-developer-mode-fix-error-0x80004005</id>
<content type="html" xml:base="https://wiseindy.com/blog/windows/windows-10-developer-mode-fix-error-0x80004005/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This is from 2017. You no longer need Developer Mode to use Windows Subsystem for Linux, so if that’s why you’re here, skip this fix and simply run <code>wsl --install</code> from an administrator Command Prompt.</p>
</div>
<p>“Developer mode package failed to install. Error code 0x80004005”. A few people, including me, faced issues when trying to enable developer mode in Windows 10. This guide will show you how to fix it.</p>
<!--more-->
<h2 id="why-this-happens">Why this happens?</h2>
<p>After quite some digging and research online, I found that this problem is related to WSUS (Windows Server Update Services). If you’re in an environment where your PC gets updates from WSUS, you can face this problem. Luckily, it’s a straightforward fix.</p>
<h2 id="step-1">Step 1:</h2>
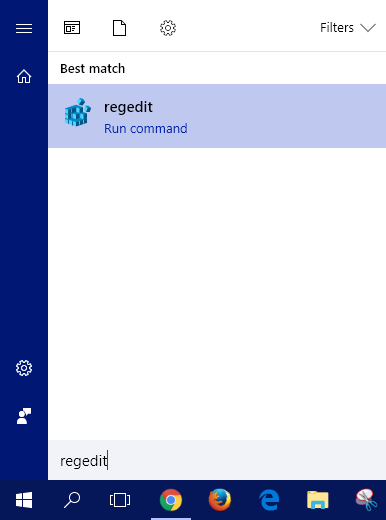
<p>Click <strong>Start</strong> and type <code>regedit</code>. Open it.</p>
<p><img src="/assets/images/posts/2017-04-26-windows-10-developer-mode-fix-error-0x80004005-001.png" alt="Click start and search for regedit" title="Click start and search for regedit"></p>
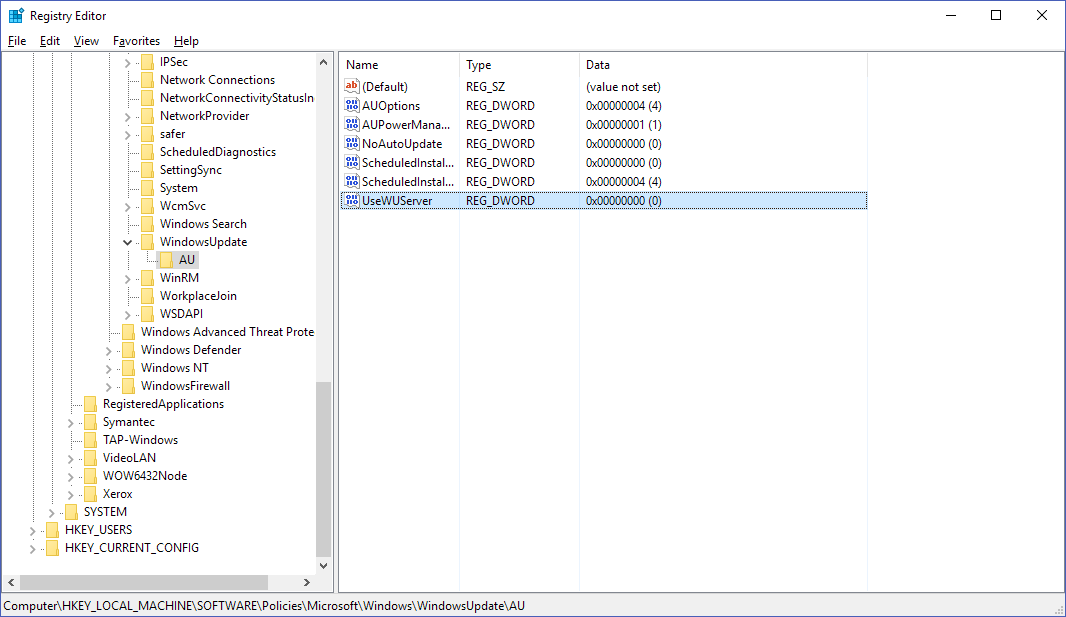
<p>Navigate to <code>HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU</code> in <strong>regedit</strong></p>
<p><img src="/assets/images/posts/2017-04-26-windows-10-developer-mode-fix-error-0x80004005-002.png" alt="Navigate to key in regedit" title="Navigate to key in regedit"></p>
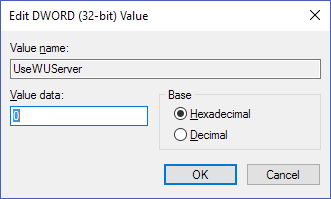
<p>Double click <strong>UseWUServer</strong> and set the value to <strong>0</strong></p>
<p><img src="/assets/images/posts/2017-04-26-windows-10-developer-mode-fix-error-0x80004005-003.png" alt="Set UseWUServer to 0" title="Set UseWUServer to 0"></p>
<h2 id="step-2">Step 2:</h2>
<p>Restart your PC. Now try to enable developer mode again. This time you will not see the error 0x80004005 and it should be enabled successfully.</p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/151415985@N06/36819065315">Wallboat</a> (CC0, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Windows"/>
<category term="windows 10"/><category term="developer"/><category term="developer mode"/><category term="shell"/><category term="bash shell"/><category term="subsystem"/><category term="guide"/><category term="linux"/><category term="ubuntu"/><category term="UseWUServer"/><category term="regedit"/><category term="error 0x80004005"/><category term="Guides"/>
</entry>
<entry>
<title type="html">Enabling Linux Bash Shell in Windows 10</title>
<link href="https://wiseindy.com/blog/windows/enabling-linux-bash-shell-in-windows-10/" rel="alternate" type="text/html" title="Enabling Linux Bash Shell in Windows 10"/>
<published>2017-04-26T05:43:44.000Z</published>
<updated>2017-04-26T05:43:44.000Z</updated>
<id>https://wiseindy.com/blog/windows/enabling-linux-bash-shell-in-windows-10</id>
<content type="html" xml:base="https://wiseindy.com/blog/windows/enabling-linux-bash-shell-in-windows-10/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This guide is from 2017, back when Windows Subsystem for Linux was still in beta. A lot has changed since then. You don’t need Developer Mode anymore, and you can skip pretty much every step below. On Windows 10 (version 2004 or later) or Windows 11, just open Command Prompt as administrator, type <code>wsl --install</code> and restart your PC. That’s it!</p>
</div>
<p>Windows 10 (the new Anniversary update, specifically) has a new feature called “Windows Subsystem for Linux”. It’s basically a full-fledged Ubuntu based bash shell running directly under Windows. Pretty cool, eh? This guide will show you how exactly to enable it.</p>
<!--more-->
<h2 id="what-you-need">What you need:</h2>
<ul>
<li>A PC running a 64-bit version of Windows 10 Anniversary Update build 14393 or later (Step 1 shows you how to check your Windows 10 version).</li>
<li>And as always, an internet connection.</li>
</ul>
<h2 id="step-1">Step 1:</h2>
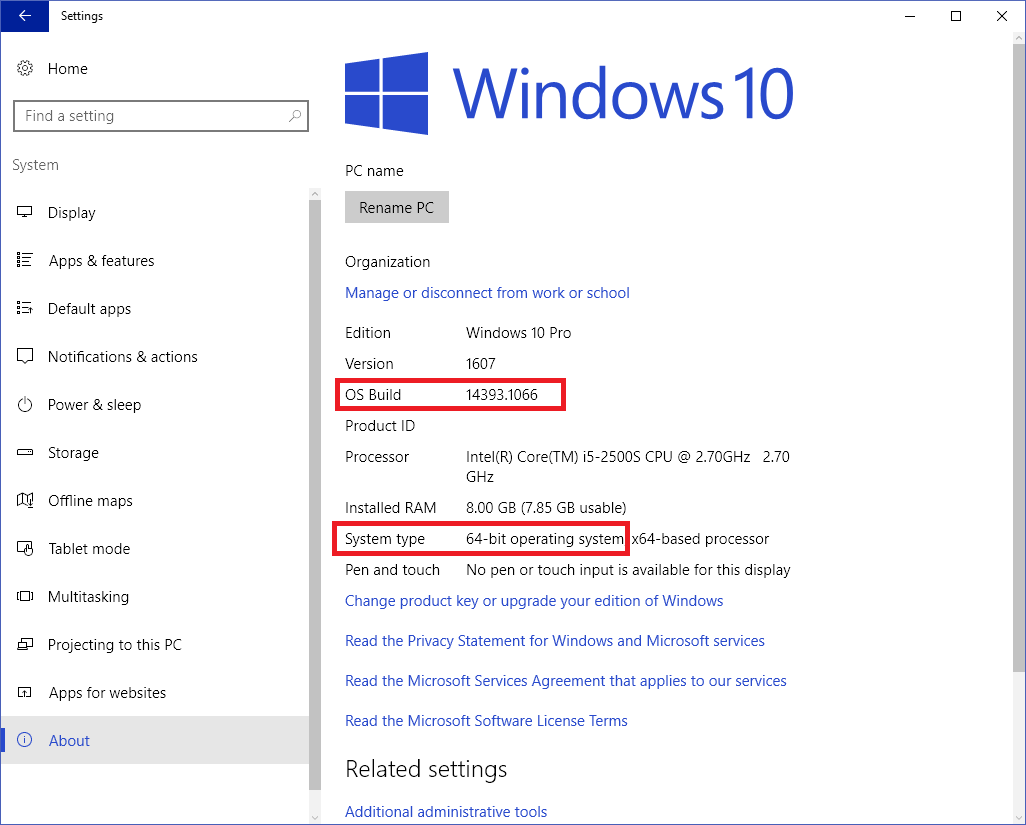
<p>First, let’s find out whether your Windows 10 is build 14393 or later.</p>
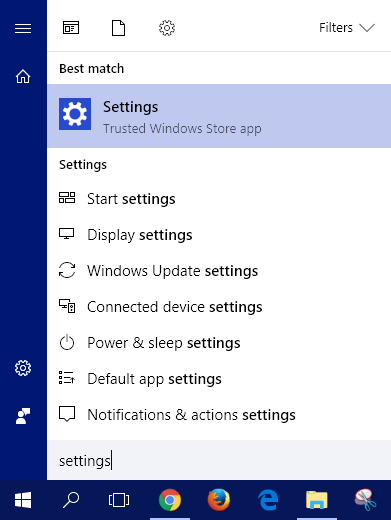
<p>To do this, simply open <strong>Settings</strong></p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-001.png" alt="Search for Settings in the Start menu" title="Search for Settings in the Start menu"></p>
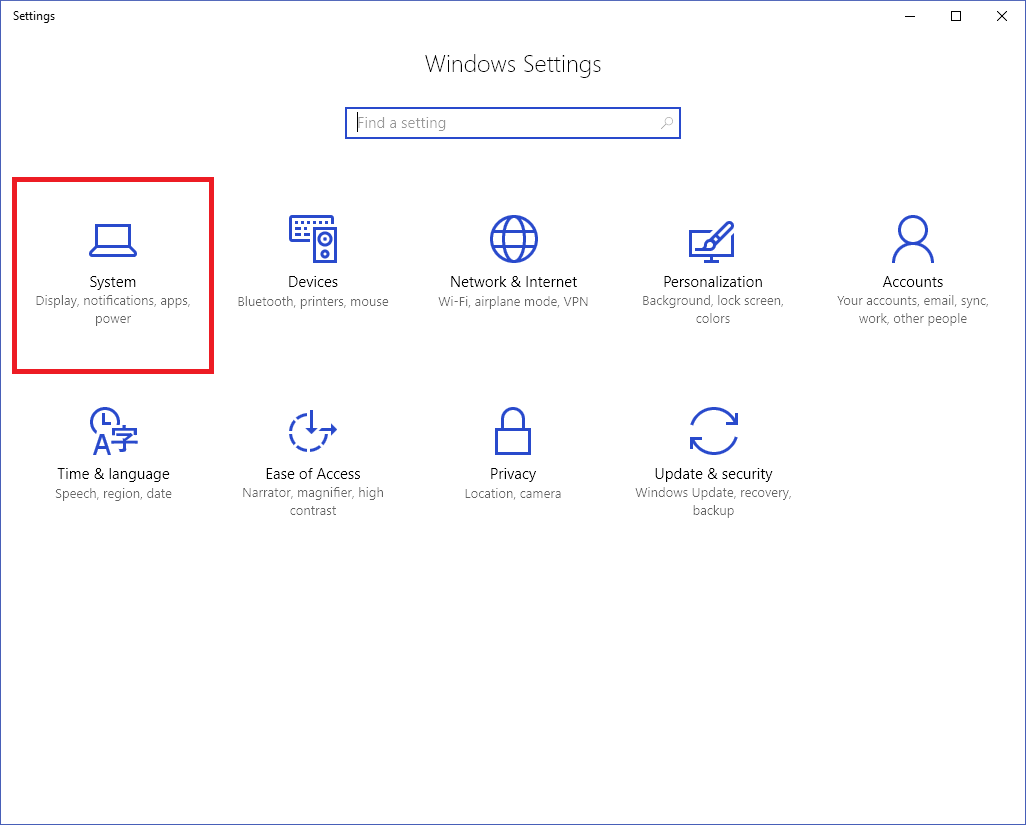
<p>Click on <strong>System</strong></p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-002.png" alt="Select System" title="Select System"></p>
<p>Scroll to the end and click on <strong>About</strong>.
Here you’ll see your <strong>OS Build</strong> number. This should be equal to or higher than <strong>14393</strong>. Also, verify if your Windows 10 installation is 64 bit.</p>
<p>If your build number is less than <strong>14393</strong>, check for updates.</p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-003.png" alt="Click on About" title="Click on About"></p>
<h2 id="step-2">Step 2:</h2>
<p>The next step is to enable <strong>Developer Mode</strong> in Windows 10.</p>
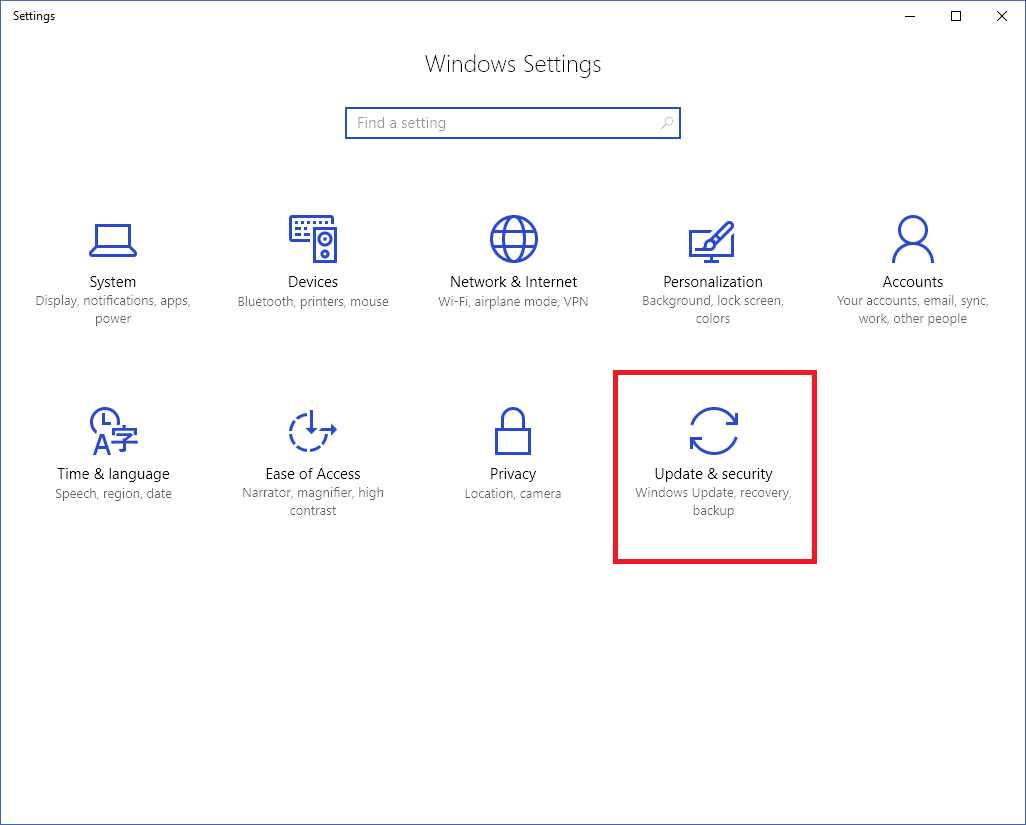
<p>Open <strong>Settings</strong> again. Select <strong>Update &amp; security</strong>.</p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-004.png" alt="Select Update &amp; security in Settings" title="Select Update &amp; security in Settings"></p>
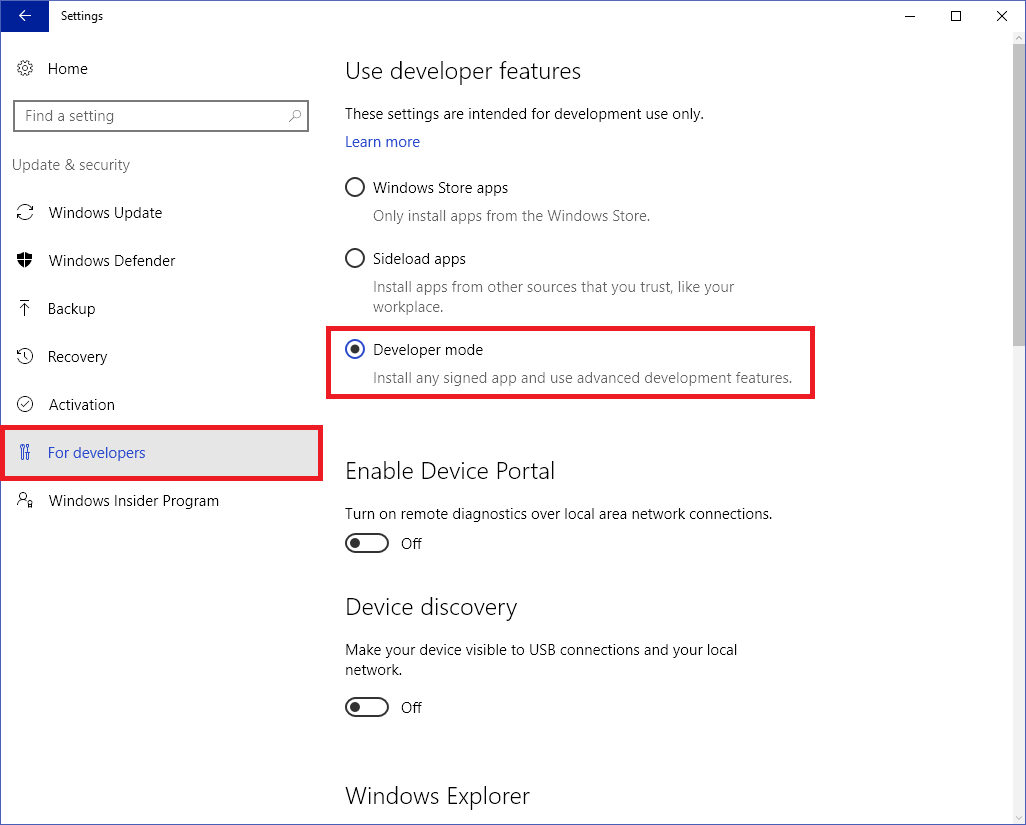
<p>Click on <strong>For developers</strong> and enable <strong>Developer mode</strong>. If it asks you to restart the PC, go ahead and restart.</p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-005.png" alt="Enable developer mode in Windows 10" title="Select For developers and enable developer mode"></p>
<p><strong>Note:</strong> <a href="/blog/windows/windows-10-developer-mode-fix-error-0x80004005/">If you get an error message <strong>Developer mode package failed to install. Error code 0x80004005</strong> while trying to enable developer mode, please click here to see how to fix it</a></p>
<h2 id="step-3">Step 3:</h2>
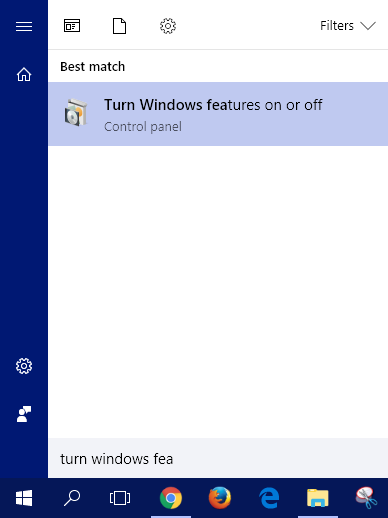
<p>Now, let’s enable <strong>Windows Subsystem for Linux</strong>. Click the <strong>Start</strong> button and search for <strong>Turn Windows features on or off</strong>.</p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-006.png" alt="Search for Turn Windows features on or off" title="Search for Turn Windows features on or off"></p>
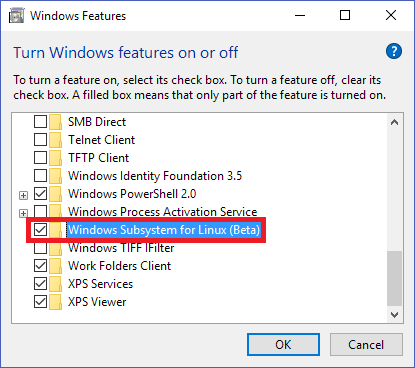
<p>Check <strong>Windows Subsystem for Linux (Beta)</strong> to enable it and click <strong>OK</strong></p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-007.png" alt="Enable Windows Subsystem for Linux (Beta)" title="Enable Windows Subsystem for Linux (Beta)"></p>
<p>Restart your PC when it prompts you to.</p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h2 id="step-4">Step 4:</h2>
<p>After you’ve rebooted your PC, open a command prompt window (click the Start button and type <code>cmd</code>).</p>
<p>Type <code>bash</code> and hit enter.</p>
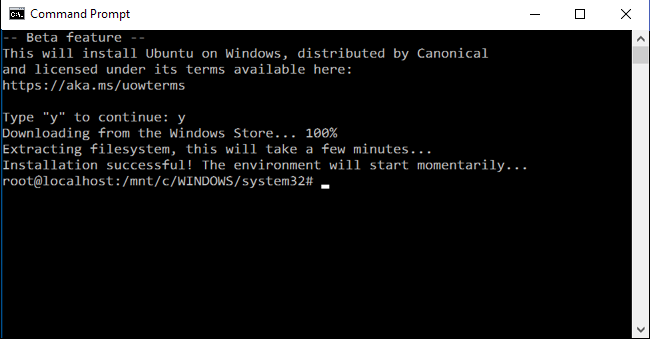
<p>Since this is the first time you’re running <code>bash</code>, you’ll be asked whether you want to install it. Type <code>y</code> and hit enter to proceed.</p>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-008.png" alt="Installing bash via command prompt" title="Installing bash via command prompt"></p>
<p>After the installation is complete, you will be asked to create a new UNIX username and password. This user account is for the new Ubuntu environment and in no way related to your Windows account.</p>
<p>Well, that’s all there is. You should have a bash prompt now and can run linux commands.</p>
<h2 id="step-5">Step 5:</h2>
<p>To start <code>bash</code> you can use two ways:</p>
<ul>
<li>Simply open any command prompt window and type <code>bash</code>. It will start the Ubuntu command line environment.</li>
<li>Click the Start button and search for <strong>bash</strong>. Open <strong>Bash on Ubuntu for Windows</strong>.</li>
</ul>
<p><img src="/assets/images/posts/2017-04-26-enabling-linux-bash-shell-in-windows-10-008.png" alt="Launching Bash on Ubuntu for Windows" title="Search for Bash on Ubuntu for Windows"></p>
<p>That’s it!</p>
<p><strong>Note:</strong> While in the Ubuntu environment, you can access your Windows drives under <code>/mnt/</code>. All Windows drives will be listed under this. You can <code>cd</code> to any directory and work with the files.</p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/78555032@N00/5080593410">Kiwithing</a> (CC0, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Windows"/>
<category term="windows 10"/><category term="bash"/><category term="shell"/><category term="bash shell"/><category term="subsystem"/><category term="guide"/><category term="linux"/><category term="ubuntu"/><category term="ubuntu 14.04"/><category term="Guides"/>
</entry>
<entry>
<title type="html">How to install or renew SSL certificate in Exchange 2010</title>
<link href="https://wiseindy.com/blog/windows/how-to-install-or-renew-ssl-certificate-in-exchange-2010/" rel="alternate" type="text/html" title="How to install or renew SSL certificate in Exchange 2010"/>
<published>2016-08-01T08:00:08.000Z</published>
<updated>2016-08-01T08:00:08.000Z</updated>
<id>https://wiseindy.com/blog/windows/how-to-install-or-renew-ssl-certificate-in-exchange-2010</id>
<content type="html" xml:base="https://wiseindy.com/blog/windows/how-to-install-or-renew-ssl-certificate-in-exchange-2010/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This post is from 2016, and Exchange 2010 reached end of support back in October 2020. The overall process (create a CSR, get it signed, import it, assign services) is still the same in newer versions, but you’ll be doing it from the Exchange Admin Center or PowerShell instead of the old Exchange Management Console.</p>
</div>
<p>You will need to create and assign a new SSL certificate if you’re putting up a new Exchange server into production or renewing it for an existing server. The steps are fairly straightforward, however it may seem daunting and completely foreign for new users who aren’t familiar with certificates.</p>
<!--more-->
<p>This guide will show you how to create a CSR (Certificate Signing Request) using your Exchange server and subsequently generating a new SSL cert and installing it.</p>
<p>Here’s a brief overview of what we will be doing in this guide:</p>
<ol>
 	<li>Create a certificate signing request (CSR) in Exchange.</li>
 	<li>Buy a new certificate from one of many SSL providers (GoDaddy in this case - process should be similar for other providers).</li>
 	<li>Use the CSR to create a new certificate on GoDaddy and download it</li>
 	<li>Install this in our Exchange server.</li>
</ol>
<h3>What you need:</h3>
<ul>
 	<li>Microsoft Exchange Server
<ul>
 	<li>In this guide, we are using Microsoft Exchange 2010.</li>
</ul>
</li>
 	<li>A commercial Certificate Authority such as <a target="_blank" href="https://www.digicert.com/">DigiCert</a>, <a target="_blank" href="https://www.godaddy.com/">GoDaddy</a>, etc.
<ul>
 	<li>In this guide, we are using GoDaddy.</li>
</ul>
</li>
</ul>
<h3>Step 1:</h3>
The first step is to generate a Certificate Signing Request. This is a requisite for generating your SSL certificate.
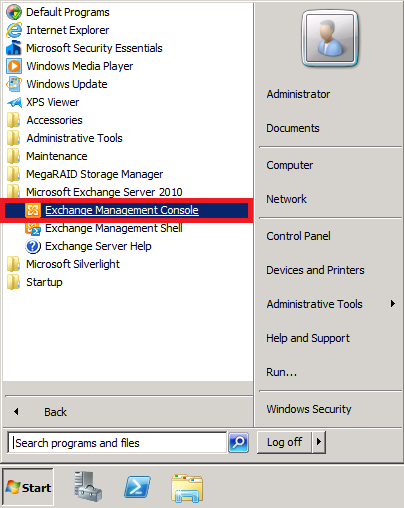
<p>Open up your <strong>Exchange Management Console</strong></p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-01.png"><img class="alignnone size-full wp-image-1028" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-01.png" alt="how-to-install-ssl-certificate-in-exchange-2010-01" /></a></p>
<h3>Step 2:</h3>
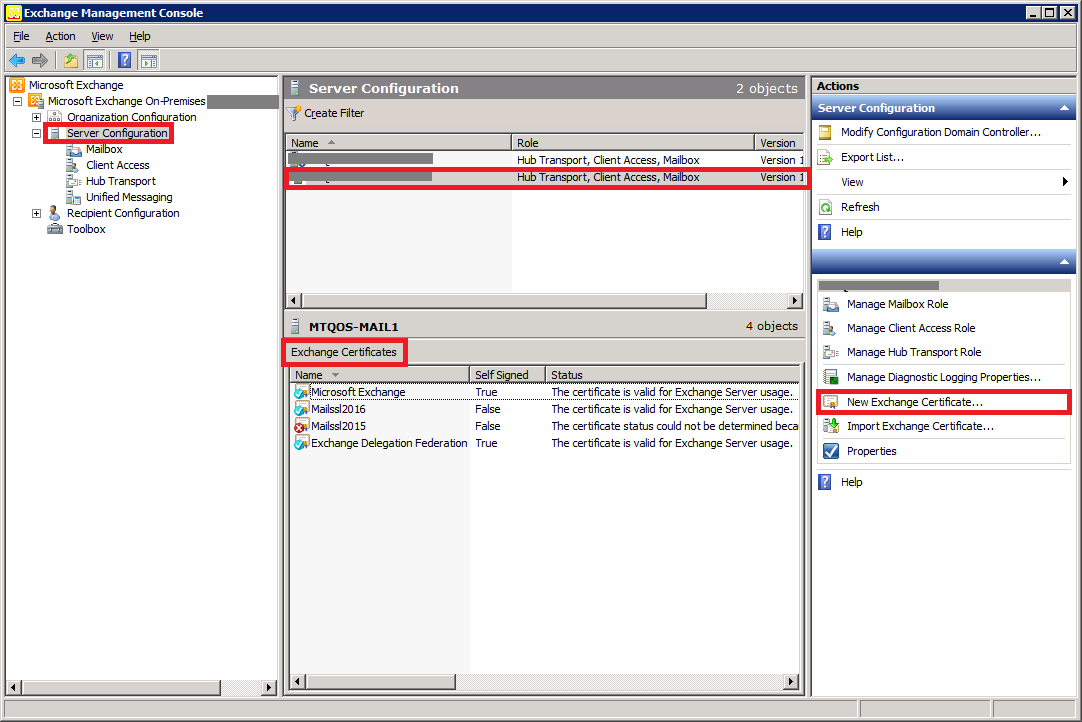
Navigate to <strong>Server Configuration &gt; Select your server</strong> (from the Server Configuration list)<strong> &gt; Exchange Certificates</strong> tab and click on <strong>New Exchange Certificate</strong>.
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-02.png"><img class="alignnone size-full wp-image-1029" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-02.png" alt="how-to-install-ssl-certificate-in-exchange-2010-02" /></a></p>
<h3>Step 3:</h3>
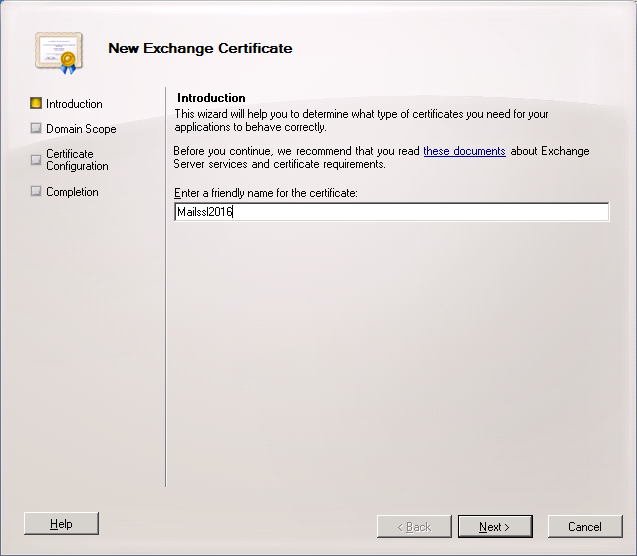
In the <strong>New Exchange Certificate</strong> Wizard, enter a name for your certificate. It can be anything you want. Click <strong>Next</strong>.
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-03_01.png"><img class="alignnone size-full wp-image-1228" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-03_01.png" alt="how-to-install-ssl-certificate-in-exchange-2010-03_01" /></a></p>
<h3>Step 4:</h3>
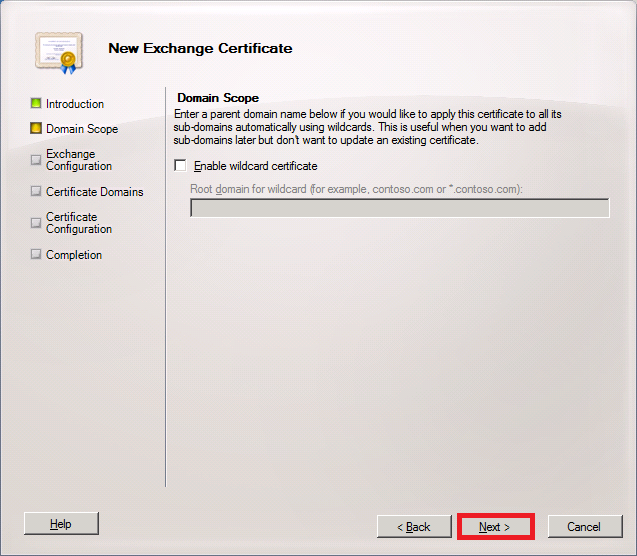
If you want to apply the certificate to <strong>all</strong> your sub domains, check <strong>Enable wildcard certificate</strong>. In my case, I wish to apply this certificate to 2 subdomains (not all), so I leave it unchecked.
<img class="alignnone size-full wp-image-1032" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-0.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-0" />
<h3>Step 5:</h3>
On the next page, you'll need to provide your Exchange Server configuration. Select whatever is applicable for <strong>each section</strong>.
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-1.png"><img class="alignnone size-full wp-image-1033" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-1.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-1" /></a></p>
<p>In my case, OWA (Outlook Web App/Access) is being accessed from the web. This is why I enable the second option “Outlook Web App is on the Internet” in the below image. The URL should be automatically populated.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-2.png"><img class="alignnone size-full wp-image-1034" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-2.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-2" /></a></p>
<p>Go through each of the sections below and verify if everything you need is selected. In my case, I didn’t need to change anything other than the Outlook Web App part in the above step. I left everything else as it is.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-3.png"><img class="alignnone size-full wp-image-1035" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-3.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-3" /></a></p>
<p>Some more pics to help you cross-verify your info.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-4.png"><img class="alignnone size-full wp-image-1036" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-4.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-4" /></a></p>
<p>If you use POP/IMAP, check the appropriate check boxes or leave them unchecked (as in my case since I don’t use it).</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-5.png"><img class="alignnone size-full wp-image-1037" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-5.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-5" /></a></p>
<p>Click Next.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-6.png"><img class="alignnone size-full wp-image-1038" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-04-alt-6.png" alt="how-to-install-ssl-certificate-in-exchange-2010-04-alt-6" /></a></p>
<h3>Step 6:</h3>
On this page, enter the details of your organization. Everything should be self-explanatory. At the bottom it asks you to specify the location of the <strong>Certificate Request File Path</strong> also known as a <strong>Certificate Signing Request</strong> or <strong>CSR</strong> in short.
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-05.png"><img class="alignnone size-full wp-image-1039" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-05.png" alt="how-to-install-ssl-certificate-in-exchange-2010-05" /></a></p>
<p>Specify the location and click <strong>Save</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-06.png"><img class="alignnone size-full wp-image-1040" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-06.png" alt="how-to-install-ssl-certificate-in-exchange-2010-06" /></a></p>
<p>Verify the information and click <strong>New</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-07.png"><img class="alignnone size-full wp-image-1041" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-07.png" alt="how-to-install-ssl-certificate-in-exchange-2010-07" /></a></p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h3>Step 7:</h3>
If all goes well, which it should, you will find that your CSR is generated and saved it in the location you specified. It's basically a text file with a <code>.req</code> extension. We will need this file in a while.
<p><a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-08.png"><img class="alignnone size-full wp-image-1042" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-08.png" alt="how-to-install-ssl-certificate-in-exchange-2010-08" /></a> <a target="_blank" href="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-09.png"><img class="alignnone size-full wp-image-1043" src="/wp-content/uploads/2015/08/how-to-install-ssl-certificate-in-exchange-2010-09.png" alt="how-to-install-ssl-certificate-in-exchange-2010-09" /></a></p>
<h3>Step 8:</h3>
Log in to your SSL provider and buy an SSL certificate if you haven't bought one already.
<p>Make sure you buy a <strong>Unified Communications Certificate</strong> <strong>(UCC)</strong> (also known as a <strong>Multiple Domain SSL</strong> or <strong>SAN</strong> certificate). A <strong>UCC/SAN</strong> certificate will allow you to secure multiple domains. You need this for Microsoft Exchange. More information here: <a target="_blank" href="https://www.godaddy.com/help/what-is-a-multiple-domain-ucc-ssl-certificate-3908"><a href="https://www.godaddy.com/help/what-is-a-multiple-domain-ucc-ssl-certificate-3908">https://www.godaddy.com/help/what-is-a-multiple-domain-ucc-ssl-certificate-3908</a></a></p>
<p>In this tutorial, I’m using GoDaddy, but the steps should be more or less the same for other providers.</p>
<h3>Step 9:</h3>
After you buy your SSL certificate, you'll have to provide it your CSR that was generated in <strong>Step 7</strong>.
<p>In my case, I’m <em>renewing</em> my certificate instead of purchasing a new one, so some screens may be different for you. If you’re renewing your certificate, you’ll have to <strong>re-key</strong> your certificate. Again, that means you have to provide your <strong>CSR</strong> from step 7.</p>
<p>Login to your SSL provider. Open your CSR (.req) file with notepad. Copy everything and paste it wherever your SSL provider asks you to.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-18.png"><img class="alignnone size-full wp-image-1212" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-18.png" alt="how-to-install-ssl-certificate-in-exchange-2010-18" /></a></p>
<h3>Step 10:</h3>
Once you provide your CSR, you'll have to wait for a bit till your domain and other details are verified. You may even need to prove your domain ownership. In case you have to, then your SSL provider will give you the steps to do so.
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-10.png"><img class="alignnone size-full wp-image-1211" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-10.png" alt="how-to-install-ssl-certificate-in-exchange-2010-10" /></a></p>
<h3>Step 11:</h3>
Once your certificate is ready, click the <strong>Download</strong> button.
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-11_1.png"><img class="alignnone size-full wp-image-1214" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-11_1.png" alt="how-to-install-ssl-certificate-in-exchange-2010-11_1" /></a></p>
<p>From the server type drop down, select <strong>Exchange</strong> and click <strong>Download File</strong>. It will be a zip with two files. Extract it and copy this over to your Exchange server.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-12.png"><img class="alignnone size-full wp-image-1215" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-12.png" alt="how-to-install-ssl-certificate-in-exchange-2010-12" /></a></p>
<h3>Step 12:</h3>
Go to your Exchange server. Right-click your certificate in Exchange Management Console and select <strong>Complete Pending Request...</strong>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-19_0.png"><img class="alignnone size-full wp-image-1223" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-19_0.png" alt="how-to-install-ssl-certificate-in-exchange-2010-19_0" /></a></p>
<h3>Step 13:</h3>
Click the <strong>Browse</strong> button in the window that pops up.
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-14.png"><img class="alignnone size-full wp-image-1218" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-14.png" alt="how-to-install-ssl-certificate-in-exchange-2010-14" /></a></p>
<p>In the Browse window, select <strong>All Files(<em>.</em>)</strong> and then choose your certificate file that you received from your SSL provider (GoDaddy).</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-15.png"><img class="alignnone size-full wp-image-1219" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-15.png" alt="how-to-install-ssl-certificate-in-exchange-2010-15" /></a></p>
<p>Click <strong>Complete</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-16.png"><img class="alignnone size-full wp-image-1220" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-16.png" alt="how-to-install-ssl-certificate-in-exchange-2010-16" /></a></p>
<p>If everything goes well, you’ll see the following screen. Click <strong>Finish.</strong></p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-17.png"><img class="alignnone size-full wp-image-1221" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-17.png" alt="how-to-install-ssl-certificate-in-exchange-2010-17" /></a></p>
<h3>Step 14:</h3>
The new Exchange certificate should have a little blue tick on the icon now. The only thing remaining now is to assign Exchange services to this certificate. That's easily done. Right click the certificate and choose <strong>Assign Services to Certificate...</strong>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-19_2.png"><img class="alignnone size-full wp-image-1224" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-19_2.png" alt="how-to-install-ssl-certificate-in-exchange-2010-19_2" /></a></p>
<p>Step 14:</p>
<p>In the window that pops up, select your server and click <strong>Next</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-20.png"><img class="alignnone size-full wp-image-1225" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-20.png" alt="how-to-install-ssl-certificate-in-exchange-2010-20" /></a></p>
<p>Select all appropriate services for this certificate. Click <strong>Next</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-21.png"><img class="alignnone size-full wp-image-1226" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-21.png" alt="how-to-install-ssl-certificate-in-exchange-2010-21" /></a></p>
<p>If you have some services already assigned to a different certificate, Exchange will ask you to confirm if you want to overwrite it with the new one. In my case, I do want to replace it, so I click <strong>Yes</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-22.png"><img class="alignnone size-full wp-image-1227" src="/wp-content/uploads/2016/08/how-to-install-ssl-certificate-in-exchange-2010-22.png" alt="how-to-install-ssl-certificate-in-exchange-2010-22" /></a></p>
<p>Guess what? That’s it! You’ve successfully installed a new SSL certificate for your Microsoft Exchange server.</p>
<p> </p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/137424368@N06/28376593808">zsolt.palatinus</a> (public domain, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Windows"/>
<category term="certificate"/><category term="csr"/><category term="digicert"/><category term="exchange"/><category term="exchange 2010"/><category term="exchange 2013"/><category term="exchange management shell"/><category term="godaddy"/><category term="microsoft"/><category term="microsoft exchange"/><category term="request"/><category term="signing"/><category term="ssl"/><category term="trusted"/><category term="Guides"/>
</entry>
<entry>
<title type="html">How to Fix Outlook PDF Previews and Explorer thumbnails on 64-bit Windows</title>
<link href="https://wiseindy.com/blog/windows/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows/" rel="alternate" type="text/html" title="How to Fix Outlook PDF Previews and Explorer thumbnails on 64-bit Windows"/>
<published>2016-02-07T03:47:20.000Z</published>
<updated>2016-02-07T03:47:20.000Z</updated>
<id>https://wiseindy.com/blog/windows/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows</id>
<content type="html" xml:base="https://wiseindy.com/blog/windows/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows/"><![CDATA[<p>“This file cannot be previewed because of an error with the following previewer: PDF Preview Handler for Vista”.</p>
<p>You might’ve seen this pretty common error in Outlook when you cannot preview PDF files in the preview pane. This happens on 64-bit Windows.</p>
<p>Well, it’s a pretty easy fix.</p>
<!--more-->
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_02.png" rel="attachment wp-att-1159"><img class="alignnone size-full wp-image-1159" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_02.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_02" /></a></p>
<h2>The manual way to fix this error</h2>
<h3>Step 1:</h3>
Click the <strong>Start</strong> button, type <strong>regedit.exe</strong> and open it.
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_01.png" rel="attachment wp-att-1158"><img class="alignnone size-full wp-image-1158" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_01.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_01" /></a></p>
<h3>Step 2:</h3>
Once open, navigate to <code>HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Classes\
CLSID\{DC6EFB56-9CFA-464D-8880-44885D7DC193}</code>
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_03.png" rel="attachment wp-att-1160"><img class="alignnone size-full wp-image-1160" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_03.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_03" /></a></p>
<h3>Step 3:</h3>
Double-click <strong>AppID</strong> in the right column and copy paste this in the Value Data field: <code>{534A1E02-D58F-44f0-B58B-36CBED287C7C}</code>
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_04.png" rel="attachment wp-att-1161"><img class="alignnone size-full wp-image-1161" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_04.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_04" /></a></p>
<p>Click <strong>OK</strong> and close regedit. That’s it!</p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h2>The automatic way to fix this error</h2>
<h3>Step 1:</h3>
Download the Adobe Reader preview handler x64 fixer by <a target="_blank" href="https://www.pretentiousname.com/">Leo Davidson</a>, from this link: <a target="_blank" href="https://www.pretentiousname.com/adobe_pdf_x64_fix/#downl">https://www.pretentiousname.com/adobe_pdf_x64_fix/#downl</a>
<p>You could download either with installer or without. I choose to do the one without the installer.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_05.png" rel="attachment wp-att-1162"><img class="alignnone size-full wp-image-1162" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_05.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_05" /></a></p>
<h3>Step 2:</h3>
Extract the downloaded files. You'll see two folders. Open the one that says <strong>"Fix for x64 Adobe Reader preview handler"</strong>.
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_06.png" rel="attachment wp-att-1163"><img class="alignnone size-full wp-image-1163" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_06.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_06" /></a></p>
<p>Run the preview handler fix utility and click <strong>Apply Fix</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_07.png" rel="attachment wp-att-1164"><img class="alignnone size-full wp-image-1164" src="/wp-content/uploads/2016/02/how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_07.png" alt="how-to-fix-outlook-pdf-previews-and-explorer-thumbnails-on-64-bit-windows_07" /></a></p>
<p>That’s it!</p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/59505333@N03/17794651543">BU Rennes 2</a> (CC0, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Windows"/>
<category term="64"/><category term="64 bit"/><category term="acrobat"/><category term="adobe"/><category term="adobe acrobat"/><category term="adobe acrobat reader"/><category term="adobe pdf preview handler for vista"/><category term="adobe reader"/><category term="microsoft outlook"/><category term="outlook"/><category term="pdf"/><category term="pdf handler"/><category term="pdf previewer"/><category term="reader"/><category term="regedit"/><category term="vista"/><category term="windows 10"/><category term="windows 7"/><category term="windows 8"/><category term="windows 8.1"/><category term="x64"/><category term="Guides"/>
</entry>
<entry>
<title type="html">How to change primary domain of free or paid Google Apps account.</title>
<link href="https://wiseindy.com/blog/web/how-to-change-primary-domain-of-free-or-paid-google-apps-account/" rel="alternate" type="text/html" title="How to change primary domain of free or paid Google Apps account."/>
<published>2016-01-31T08:05:38.000Z</published>
<updated>2016-01-31T08:05:38.000Z</updated>
<id>https://wiseindy.com/blog/web/how-to-change-primary-domain-of-free-or-paid-google-apps-account</id>
<content type="html" xml:base="https://wiseindy.com/blog/web/how-to-change-primary-domain-of-free-or-paid-google-apps-account/"><![CDATA[<div class="notice notice--danger">
<p><strong>Heads up (as of November 2026):</strong> This method no longer works. Readers started reporting it broken back in February 2018, and Google Apps has since become Google Workspace. I’m leaving this post up for reference, but don’t expect these steps to work today.</p>
</div>
<p>Back in the day, Google Apps for Business (Work) was free for up to 10 users. Sadly, that is no longer the case. If you are one of the lucky ones to have grabbed an account during those times and you’re now looking for ways to change that domain, well, you’ve come to the right place. This guide will show you how to do this AND it’s applicable for both free Google Apps accounts and paid Google Apps subscriptions.</p>
<!--more-->
<p>If you have a paid account, you can simply create a new alias for your existing domain. However, you cannot do this if you have one of the “legacy” free accounts (which are now discontinued - however if you created one back in the day, you can still use them - at least at the time of writing this post).</p>
<p>There can be many reasons for you to change your primary domain. For me it was because I lost ownership of my old domain and didn’t want my free Google Apps account sitting and gathering dust.</p>
<p>Google has a couple of support articles - <a target="_blank" href="https://support.google.com/a/answer/54819?hl=en">here</a> and <a target="_blank" href="https://support.google.com/a/answer/6301932">here</a> - that can help you achieve this. However even with the help of these articles it took me quite a while to figure it out. This is why I wrote this step-by-step guide to make it easier for you guys.</p>
<p>So, enough talk. Let’s get started.</p>
<h3>What do you need:</h3>
<ul>
	<li>A free or paid Google Apps account.</li>
	<li>Access to your <strong>new</strong> domain's registrar/hosting account (so that you can verify domain ownership when Google asks you to).</li>
</ul>
<h3>In short, this is what we will be doing:</h3>
<span style="text-decoration: underline;"><strong>If you have a "legacy" free account</strong>:</span> We are going to <strong>temporarily</strong> convert our <strong>free</strong> account to a free 30 day enterprise trial account. Then we are going to add in another domain to your account and make it the primary one. Next, we disable and remove the old domain and cancel our trial to convert our paid account back to free.
<p><span style="text-decoration: underline;"><strong>If you have a paid Google Apps for Work subscription</strong>:</span> We are going to add in another domain to your account and then make it the primary one.</p>
<blockquote><span style="text-decoration: underline;">Note:</span> If you have a paid Google Apps subscription, skip to <strong>Step 3</strong>.</blockquote>
<h3>Step 1:</h3>
Log into your existing Google Apps account. Navigate to <a target="_blank" href="https://apps.google.com">https://apps.google.com</a> and sign in.
<p>Alternatively, you could navigate to <a target="_blank" href="https://www.google.com/work/apps/business/"><a href="https://www.google.com/work/apps/business/">https://www.google.com/work/apps/business/</a></a> or even use your domain’s custom Google Apps URL.</p>
<p>For example, if your domain is <a target="_blank" href="https://wiseindy.com">wiseindy.com</a>, simply navigate to <a target="_blank" href="https://google.com/a/example.com"><a href="https://google.com/a/">https://google.com/a/</a><strong>wiseindy.com</strong></a>.</p>
<h3>Step 2:</h3>
Once you're logged in, click on the big red <strong>Upgrade Now</strong> button on the right hand sidebar.
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-01.png" rel="attachment wp-att-1143"><img class="alignnone size-full wp-image-1143" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-01.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-01" /></a></p>
<p>Enter in your information, check the terms and conditions check box and click <strong>I accept! Upgrade my account</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-02.png" rel="attachment wp-att-1145"><img class="alignnone size-full wp-image-1145" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-02.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-02" /></a></p>
<h3>Step 3:</h3>
Next, go back to the admin console and click <strong>Domains</strong>. If you don't see the <strong>Domains</strong> tile, click the <strong>Show More</strong> link at the bottom and then select <strong>Domains</strong>.
<p>Then click on <strong>Add/Remove</strong> domains.</p>
<p>Alternatively, you can just navigate to the domains page directly via this link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:"><a href="https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains">https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains</a>:</a></p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-03.png" rel="attachment wp-att-1146"><img class="alignnone size-full wp-image-1146" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-03.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-03" /></a></p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-04.png" rel="attachment wp-att-1147"><img class="alignnone size-full wp-image-1147" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-04.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-04" /></a></p>
<p>Disable the test domain alias by clicking the <strong>Deactivate</strong> button as shown below. A popup box will ask you to confirm this action. Confirm it.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-05.png" rel="attachment wp-att-1148"><img class="alignnone size-full wp-image-1148" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-05.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-05" /></a></p>
<p>After the test domain alias is deactivated, click the <strong>Add a domain or domain alias</strong> button at the top.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-06.png" rel="attachment wp-att-1149"><img class="alignnone size-full wp-image-1149" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-06.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-06" /></a></p>
<h3>Step 4:</h3>
Enter the new domain name. Follow Google's verification steps to verify ownership for your new domain. This should be pretty straightforward if you have access to your domain registrar/hosting account. Since Google shows you step by step how to verify your domain, I won't cover it here.
<h3>Step 5:</h3>
If everything goes well, you should have your new domain added to your Google Apps account. You can confirm by going to the <strong>Domains</strong> panel from the admin console (here is the direct link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:">https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:</a>)
<p>You’ll notice that even though the new domain has been successfully added, the old domain is still marked as the <strong>primary</strong> one. Let’s change that.</p>
<p>Navigate to <a target="_blank" href="https://developers.google.com/admin-sdk/directory/v1/reference/customers/update"><a href="https://developers.google.com/admin-sdk/directory/v1/reference/customers/update">https://developers.google.com/admin-sdk/directory/v1/reference/customers/update</a></a></p>
<p>Make sure you’re logged into your existing Google Apps account (you can see your email address in the top right corner).</p>
<p>Click <strong>Try it now.</strong></p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-07.png" rel="attachment wp-att-1150"><img class="alignnone size-full wp-image-1150" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-07.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-07" /></a></p>
<p>Enter the information as shown in the screenshot below.</p>
<ul>
	<li><code><strong>customerKey:</strong> my_customer</code></li>
	<li><code><strong>fields</strong>: customerDomain</code></li>
	<li><code><strong>Request body</strong>: { "customerDomain":"newwiseindy.com" }</code></li>
</ul>
For <strong>Request body</strong>, you don't need to type the brackets and all that. They will automatically appear when you click the <strong>Request body</strong> field. Simply choose <strong>customerDomain</strong> from the dropdown and then <strong>type in your <span style="text-decoration: underline;">new domain</span></strong> (the one that you want as your <strong>primary</strong> domain).
<p>Click <strong>Authorize and Execute</strong>.</p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<p>A couple of popups might show up asking you to authorize this with your Google account, Authorize everything.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-08.png" rel="attachment wp-att-1151"><img class="alignnone size-full wp-image-1151" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-08.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-08" /></a></p>
<p>Guess what? Your secondary domain (the one you typed above) is now your <strong>primary</strong> domain! You can confirm by going to the <strong>Domains</strong> panel from the admin console (direct link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:"><a href="https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains">https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains</a>:</a>)</p>
<h3>Step 6:</h3>
If you are using a <strong>paid</strong> Google Apps account, you can stop here.
<p>However if you are using a <strong>free</strong> account, <span style="text-decoration: underline;"><strong>make sure you follow these steps to DOWNGRADE your 30 day trial back to the free account</strong></span>.</p>
<p>If you do not downgrade within 30 days, you’ll lose your free account (in the sense that you’ll have to pay for it beyond the 30 days time period).</p>
<p>You can only downgrade if you have only one domain in your account. But we now have two. The old domain and the new domain (which was just promoted to primary).</p>
<p>Let’s remove the old domain (that USED to be the primary once upon a time).</p>
<ul>
	<li>Go to the <strong>Domains</strong> panel from the admin console (direct link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:">https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:</a>)</li>
	<li>Delete the old domain
<ul>
	<li>If you're unable to delete it (ie, even after clicking <strong>Delete</strong>, the domain still stays, make sure the <strong>Test domain alias</strong> is deactivated. If that is active, you won't be able to delete the old domain).</li>
</ul>
</li>
</ul>
<h3>Step 7:</h3>
Let's convert our 30 day trial back to a free account. In the admin console, click on <strong>Billing</strong>. Alternatively, directly open it via this link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#DomainSettings/notab=1&amp;subtab=subscriptions">https://admin.google.com/AdminHome?pli=1&amp;fral=1#DomainSettings/notab=1&amp;subtab=subscriptions</a>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-09.png" rel="attachment wp-att-1152"><img class="alignnone size-full wp-image-1152" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-09.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-09" /></a></p>
<p>Click the 3 vertical dots and in the dropdown select <strong>Cancel Subscription</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-10.png" rel="attachment wp-att-1153"><img class="alignnone size-full wp-image-1153" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-10.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-10" /></a></p>
<p>Choose <strong>Downgrade to Google Apps</strong>.</p>
<p><strong><span style="color: #ff0000;">Do not choose Cancel Google Apps for Work. This will completely delete your account. Yes. Free, paid, everything. </span></strong>Make sure you choose <strong>Downgrade to Google Apps</strong>. If you do not see the <strong>“downgrade”</strong> option, then make sure that you have only <strong>one</strong> domain in your <strong>Domains</strong> panel (direct link: <a target="_blank" href="https://admin.google.com/AdminHome?pli=1&amp;fral=1#Domains:"><a href="https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains">https://admin.google.com/AdminHome?pli=1&amp;amp;fral=1#Domains</a>:</a>)</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-11.png" rel="attachment wp-att-1154"><img class="alignnone size-full wp-image-1154" src="/wp-content/uploads/2016/01/how-to-change-primary-domain-of-free-or-paid-google-apps-account-11.png" alt="how-to-change-primary-domain-of-free-or-paid-google-apps-account-11" /></a></p>
<p>Click <strong>Continue</strong>.</p>
<p>That’s it. You’ve successfully changed the primary domain of your free/paid Google Apps account!</p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/14674348@N04/7031591233">DennisM2</a> (CC0, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Web"/>
<category term="domain"/><category term="google"/><category term="google apps"/><category term="google apps for business"/><category term="google apps for work"/><category term="Guides"/>
</entry>
<entry>
<title type="html">How to set up Shrew Soft IPSec VPN Client for WatchGuard</title>
<link href="https://wiseindy.com/blog/windows/set-up-shrew-soft-ipsec-vpn-client-watchguard/" rel="alternate" type="text/html" title="How to set up Shrew Soft IPSec VPN Client for WatchGuard"/>
<published>2016-01-20T06:36:14.000Z</published>
<updated>2016-01-20T06:36:14.000Z</updated>
<id>https://wiseindy.com/blog/windows/set-up-shrew-soft-ipsec-vpn-client-watchguard</id>
<content type="html" xml:base="https://wiseindy.com/blog/windows/set-up-shrew-soft-ipsec-vpn-client-watchguard/"><![CDATA[<div class="notice notice--warning">
<p><strong>Heads up (as of November 2026):</strong> This post is from 2016 and parts of it are outdated. The settings in Step 3 (SHA1, 3DES and Diffie-Hellman Group 1) were common back then, but they’re considered weak today. If you’re setting this up now, go with AES, SHA-256 and Diffie-Hellman Group 14 or higher. Also, the Shrew Soft client hasn’t been updated in years, so you’re better off with WatchGuard’s own Mobile VPN client or IKEv2, which Windows supports out of the box.</p>
</div>
<p>This guide will show you how to enable Mobile VPN with IPSec for WatchGuard Firebox M300. It’s a pretty straightforward process, however it took me quite a while to figure out initially. Hope this guide makes it easier for you.</p>
<!--more-->
<p>It will also show you how to install and configure the <a target="_blank" href="https://www.shrew.net/download/vpn">Shrew Soft IPSec VPN Client</a>. In my opinion, you are better off using this client than the <a target="_blank" href="https://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/mvpn/client/mvpn-ipsec_client_about_c.html%3FTocPath%3DMobile%2520VPN%2520with%2520IPSec%7CAbout%2520the%2520IPSec%2520Mobile%2520VPN%25C2%25A0Client%7C_____0">WatchGuard IPSec Mobile VPN Monitor</a>. Old versions of this WatchGuard IPSec Mobile VPN Monitor were free, but they do not work on Windows 10. The new version of the IPSec client needs a paid subscription license. Unless you want to go this route, I would suggest using the Shrew Soft IPSec VPN Client. It’s free and you can <a target="_blank" href="https://www.shrew.net/download/vpn">download</a> it from their <a target="_blank" href="https://www.shrew.net/download/vpn">official website</a>.</p>
<p><strong>Note:</strong> While this guide was created for Firebox M300, it should work with other WatchGuard XTM devices as well.</p>
<h3>What do you need:</h3>
<ul>
	<li>An environment where a WatchGuard firewall is installed and running.</li>
	<li>Administrative access to the firewall (of course).</li>
</ul>
So let's begin, shall we?
<h3>Step 1</h3>
Fire up your browser and navigate to the web interface of your firewall. If your firewall's IP address is <code>192.168.1.1</code>, then type <code>https://192.168.1.1:8080</code> in the URL bar.
<p>After logging in, go to <strong>VPN</strong> &gt; <strong>Mobile VPN with IPSec</strong>.</p>
<p>Click on <strong>Add</strong> to add a new group.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-01.png" rel="attachment wp-att-1087"><img class="alignnone size-full wp-image-1087" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-01.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-01" /></a></p>
<h3>Step 2:</h3>
Select the <strong>General</strong> tab. Type in a <strong>Name</strong> and select Authentication Server as <strong>Firebox-DB</strong>. You can also set it to authenticate it with your domain, but for this tutorial we will use the firewall as the authentication server.
<p>Next, enter the <strong>passphrase</strong> and enter your firewall’s external IP address. This is the IP address that you use to connect to your firewall from the Internet.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-02.png" rel="attachment wp-att-1062"><img class="alignnone size-full wp-image-1062" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-02.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-02" /></a></p>
<h3>Step 3:</h3>
Select the <strong>IPSec Tunnel</strong> tab. Make the following changes as shown in the image below.
<ul>
	<li>Select <strong>Use the passphrase of the end user profile as the pre-shared key</strong>.</li>
	<li>Under <strong>Phase 1</strong><strong> Settings</strong>, select <strong>Authentication</strong> as <strong>SHA1</strong> and <strong>Encryption</strong> as <strong>3DES</strong>.</li>
	<li>Under <strong>Phase 2</strong><strong> Settings</strong>, select <strong>PFS</strong> and choose <strong>Diffie-Hellman Group 1</strong>.</li>
</ul>
<a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-03.png" rel="attachment wp-att-1063"><img class="alignnone size-full wp-image-1063" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-03.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-03" /></a>
<h3>Step 4:</h3>
Select the <strong>Resources</strong> tab. Here under <strong>Allowed Resources</strong> you can specify which IP addresses are allowed to connect through the tunnel. Click <strong>Add</strong> and type in an IP range.
<p>Next, you’ll have to specify the <strong>Virtual IP Address Pool</strong>. Whenever a device connects to your tunnel, it will be assigned an IP address from this pool.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-04.png" rel="attachment wp-att-1064"><img class="alignnone size-full wp-image-1064" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-04.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-04" /></a></p>
<div class="row">
  <div class="col-12">
  </div>
</div>
<h3>Step 5:</h3>
Finally, go the <strong>Advanced</strong> tab and set the <strong>Connect mode</strong> to <strong>Manual</strong> and <strong>Inactivity timeout</strong> to <strong>0 seconds</strong>.
<p>Click <strong>Save</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-05.png" rel="attachment wp-att-1065"><img class="alignnone size-full wp-image-1065" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-05.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-05" /></a></p>
<h3>Step 6:</h3>
The next step is to create a user which will connect to the tunnel.
<p>In your firewall web interface, navigate to <strong>Authentication</strong> &gt; <strong>Servers</strong>.</p>
<p>Select <strong>Firebox</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-06.png" rel="attachment wp-att-1066"><img class="alignnone size-full wp-image-1066" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-06.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-06" /></a></p>
<h3>Step 7:</h3>
Under <strong>Firebox Users</strong>, click <strong>Add</strong> to create a new user.
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-07.png" rel="attachment wp-att-1067"><img class="alignnone size-full wp-image-1067" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-07.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-07" /></a></p>
<h3>Step 8:</h3>
This part is pretty straight forward. Enter the <strong>Name</strong>, <strong>Description</strong>, <strong>Passphrase </strong>and<strong> timeout</strong> values.
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-08.png" rel="attachment wp-att-1068"><img class="alignnone size-full wp-image-1068" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-08.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-08" /></a></p>
<p>Under <strong>Firebox Authentication Groups</strong>, select the <strong>Group</strong> we created previously. In our case, it was <strong>WISEINDY</strong>, so we check that one.</p>
<p>Click <strong>OK</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-09.png" rel="attachment wp-att-1069"><img class="alignnone size-full wp-image-1069" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-09.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-09" /></a></p>
<h3>Step 9:</h3>
Now, navigate back to <strong>VPN</strong> &gt; <strong>Mobile VPN with IPSec</strong> in the firewall web interface.
<p>Here you can download the configuration settings for your preferred IPSec VPN Client. I prefer the free <a target="_blank" href="https://www.shrew.net/download/vpn">Shrew Soft IPSec VPN Client</a> (click to download the client).</p>
<p>From the <strong>Client</strong> dropdown box, select <strong>Shrew Soft VPN</strong> and click <strong>Generate</strong>. It will generate a <code>.vpn</code> file. Save this on your PC.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-10.png" rel="attachment wp-att-1070"><img class="alignnone size-full wp-image-1070" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-10.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-10" /></a></p>
<h3>Step 10:</h3>
Go ahead and install the Shrew Soft VPN Client on your PC. Once installed, double click the <strong>VPN Access Manager</strong> icon on your desktop to launch it.
<p>Select <strong>File</strong> &gt;<strong> Import</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-11.png" rel="attachment wp-att-1071"><img class="alignnone size-full wp-image-1071" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-11.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-11" /></a></p>
<p>Choose the <code>.vpn</code> file that was downloaded in the previous step. Click <strong>Open</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-12.png" rel="attachment wp-att-1072"><img class="alignnone size-full wp-image-1072" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-12.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-12" /></a></p>
<h3>Step 11:</h3>
A new connection will be created from the imported settings. Select this connection and click <strong>Connect.</strong>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-13.png" rel="attachment wp-att-1073"><img class="alignnone size-full wp-image-1073" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-13.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-13" /></a></p>
<p>When you click <strong>Connect</strong>, a window will pop up asking you to input credentials to connect to the tunnel.</p>
<p>Enter the <strong>Username</strong> and <strong>Password</strong> that you used to create a user in <strong>Step 8</strong>.</p>
<p>Click <strong>Connect</strong>.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-14.png" rel="attachment wp-att-1074"><img class="alignnone size-full wp-image-1074" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-14.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-14" /></a></p>
<p>If the connection is successful, you’ll see a <strong>tunnel enabled</strong> message in the window.</p>
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-15.png" rel="attachment wp-att-1075"><img class="alignnone size-full wp-image-1075" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-15.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-15" /></a></p>
<p>That’s all. You have successfully set up and configured IPSec VPN for your WatchGuard XTM device.</p>
<h3>Additional information:</h3>
In case someone needs it, here are my configuration settings that were imported into the Shrew Soft VPN client. You don't need to change anything here. The correct settings should automatically be configured when this file was generated by your firewall. I've only put up this screenshots in case someone is facing any issues and would like to double-check or compare his settings.
<p><a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-16.png" rel="attachment wp-att-1076"><img class="alignnone size-full wp-image-1076" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-16.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-16" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-17.png" rel="attachment wp-att-1077"><img class="alignnone size-full wp-image-1077" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-17.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-17" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-18.png" rel="attachment wp-att-1078"><img class="alignnone size-full wp-image-1078" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-18.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-18" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-19.png" rel="attachment wp-att-1079"><img class="alignnone size-full wp-image-1079" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-19.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-19" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-20.png" rel="attachment wp-att-1080"><img class="alignnone size-full wp-image-1080" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-20.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-20" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-21.png" rel="attachment wp-att-1081"><img class="alignnone size-full wp-image-1081" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-21.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-21" /></a> <a target="_blank" href="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-22.png" rel="attachment wp-att-1082"><img class="alignnone size-full wp-image-1082" src="/wp-content/uploads/2016/01/set-up-shrew-soft-ipsec-vpn-client-watchguard-22.png" alt="set-up-shrew-soft-ipsec-vpn-client-watchguard-22" /></a></p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/54563451@N08/14339520776">Sam Droege</a> (public domain, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Windows"/>
<category term="firebox"/><category term="firewall"/><category term="ipsec"/><category term="m300"/><category term="network"/><category term="networking"/><category term="shrew"/><category term="shrew soft"/><category term="vpn"/><category term="watchguard"/><category term="xtm"/><category term="Guides"/>
</entry>
<entry>
<title type="html">Virtual Machines: Snapshots aren’t backups</title>
<link href="https://wiseindy.com/blog/tech/virtual-machines-snapshots-arent-backups/" rel="alternate" type="text/html" title="Virtual Machines: Snapshots aren’t backups"/>
<published>2015-08-23T06:50:33.000Z</published>
<updated>2015-08-23T06:50:33.000Z</updated>
<id>https://wiseindy.com/blog/tech/virtual-machines-snapshots-arent-backups</id>
<content type="html" xml:base="https://wiseindy.com/blog/tech/virtual-machines-snapshots-arent-backups/"><![CDATA[<p>Backups, Snapshots and Archives. They are three different things, however they’re frequently confused to be the same. Does the advent of virtualization mean traditional backups can be replaced by new data protection methods such as snapshots?</p>
<!--more-->
<h3>Backups</h3>
Backing up is the process of making an additional copy of data that can be easily restored if the primary data becomes lost or unusable. Backups can be copied to external media, like portable hard drives and tape, or remote storage, like a NAS, SAN, or server at another site.
<p>Backups offer a solid solution should a major hardware or site disaster occur. Although traditional backups don’t necessarily provide the flexibility or efficiency of other methods, they offer a better long-term solution for data retention especially where backup policies dictate redundant backup copies in geographically dispersed locations.</p>
<h3>Archives</h3>
Archives are different. Imagine you back your SQL databases up to simple *.bak files on the same drive as the database, you haven't created a backup, but rather you've created an archive. An archive is a copy of your data as it exists at a point in time that doesn't meet all of the requirements to be a true backup. Assume that your SQL server crashes. You will not be able to restore your database from the archives. You'll have to first rebuild your entire server and configure it exactly as it was before and then restore from archive. Not ideal.
<p>However, archives can be very useful for quick restores and solving minor issues, but only backups truly protect your data. A backup must be able to survive a total failure of the source, not just a single hard drive failure.</p>
<h3>Snapshots</h3>
Snapshots are point-in-time copies of the data. As the name indicates, they're "snapshots" of the entire data set taken at a specific time. Snapshots are not backups. A snapshot file is only a change log of the original virtual disk. Snapshots are sometimes marketed as valid “backup solutions”. This is an incorrect and dangerous assumption.
<div class="row">
  <div class="col-12">
  </div>
</div>
<p>Snapshots <strong>are not complete copies of the original virtual machine disk files</strong>. Taking a snapshot does not create a complete copy of the original vm disk file, rather it only copies the changes that were made since the previous snapshot. Every snapshot needs the base disk and the previous snapshot file to be functional. At any point of time, to access a snapshot, you should have full access to the snapshot chain before it. If the base disks are deleted, the snapshot files are useless.</p>
<p>While there are benefits of using snapshots for development or testing purposes on non-production systems, they should not be considered as valid data protection or backups of your virtual machines.</p>
<p>A good data protection strategy combines a number of aspects that can include all of the above features.</p>
<p>While snapshots aren’t true backups, they do provide a lot of value. Short-term snapshots are great for dealing with user errors and some data corruption scenarios. More importantly, they are very fast (data can be reverted or restored in seconds). They’re extremely space-efficient and in many cases, restores can be performed very quickly. Snapshots reduce the amount of labor needed to manage an environment and are generally good enough for daily use. The issue is simply that they can’t be relied upon in a major disaster, and any true backup strategy must go beyond snapshots.</p>
<p class="credit">Header photo by <a href="https://www.flickr.com/photos/132795455@N08/17094839977">Image Catalog</a> (CC0, via Flickr)</p>
]]></content>
<author><name>Wiseindy</name></author>
<category term="Tech"/>
<category term="virtual machines"/><category term="backup"/><category term="snapshot"/>
</entry>
</feed>